
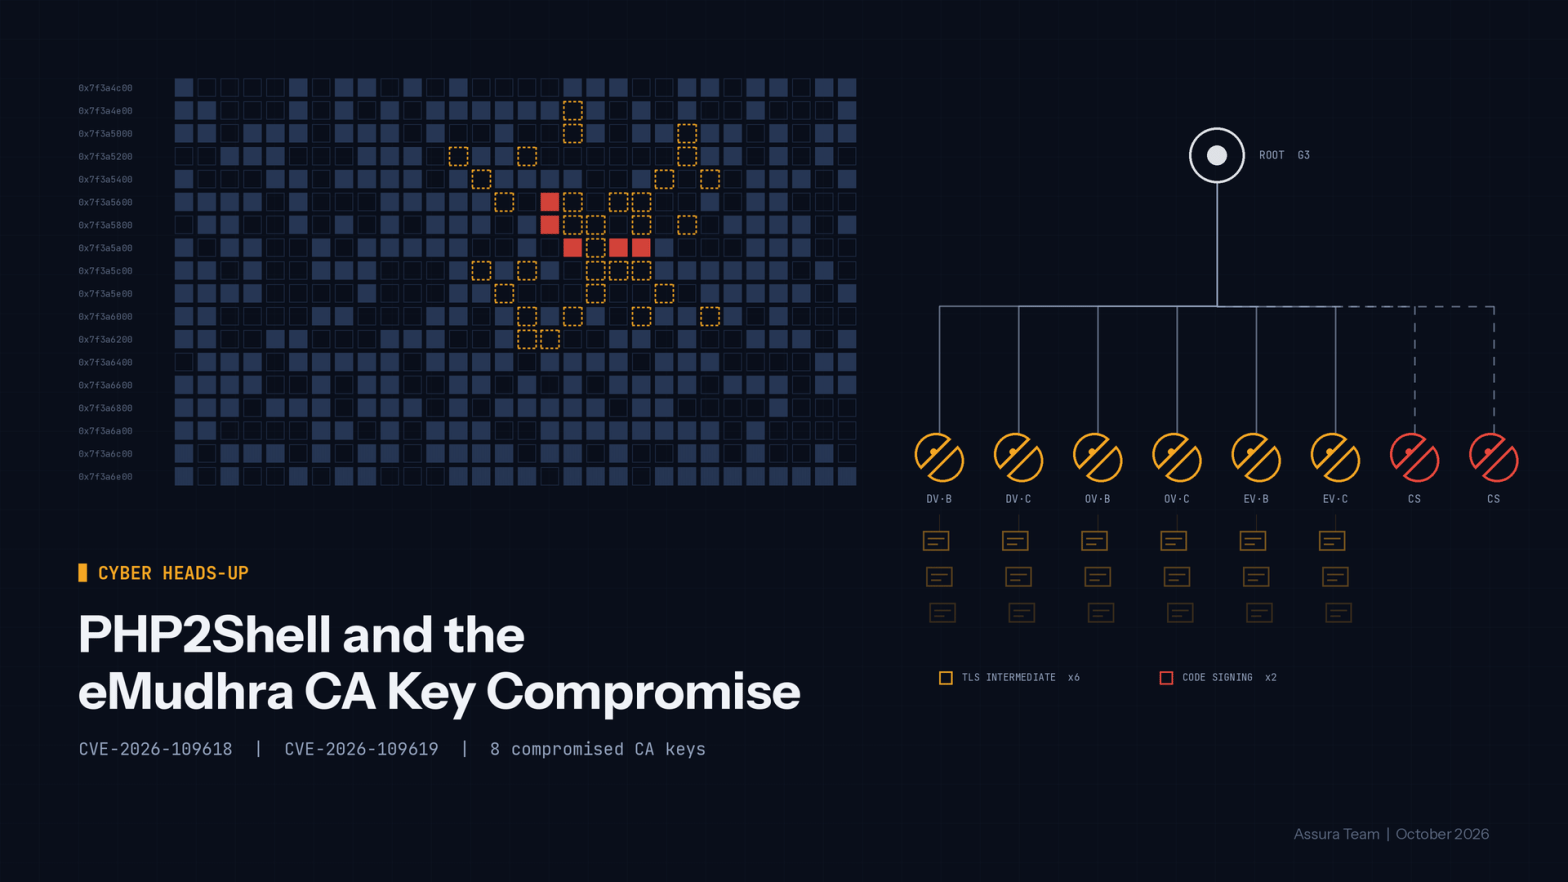
October 20 was a rough day for the internet’s plumbing. Two critical problems surfaced within hours of each other, and both sit in technology nearly every organization runs: the PHP engine behind WordPress, Drupal, Magento, and countless custom applications, and the TLS certificate trust that keeps HTTPS honest. Neither can wait for next month’s maintenance window.
Category: Cyber Heads-up
Recent Tenable Agent Update Causes False Positives in EDR Software
Good morning, Yesterday (May 25, 2026), the Assura team began receiving reports that various Endpoint Detection and Response (EDR) platforms began quarantining systems running the Tenable Vulnerability Management agent for Windows. Because this is highly unusual, our Security Operations Center (SOC) team conducted a thorough investigation out of an abundance of caution to rule out… Continue reading Recent Tenable Agent Update Causes False Positives in EDR Software
YellowKey BitLocker Bypass and GreenPlasma SYSTEM Escalation Hit Windows 11 and Server 2022/2025
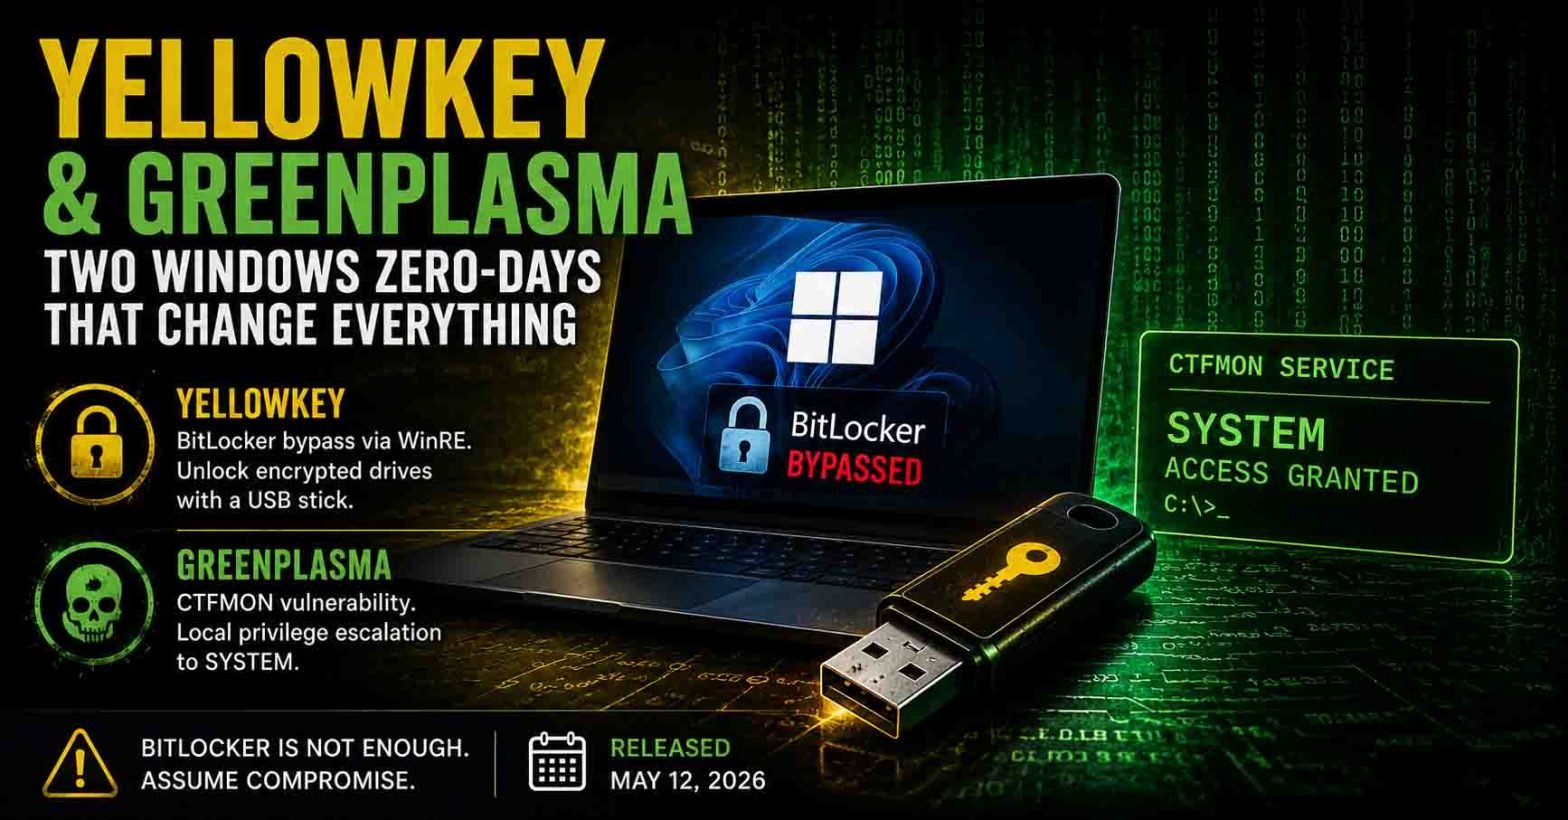
Update, May 26, 2026 Last week, we wrote about YellowKey, the BitLocker bypass that turns a missing Windows 11 laptop into a data exposure event. The proof-of-concept is public, Microsoft has assigned CVE-2026-45585 (CVSS 6.8), and a full security update still has no committed ship date. Mitigation guidance exists, but the choice between Microsoft’s WinRE… Continue reading YellowKey BitLocker Bypass and GreenPlasma SYSTEM Escalation Hit Windows 11 and Server 2022/2025
Cyber Heads Up: “Copy Fail” (CVE-2026-31431), a High-Severity Linux Kernel Privilege Escalation Vulnerability
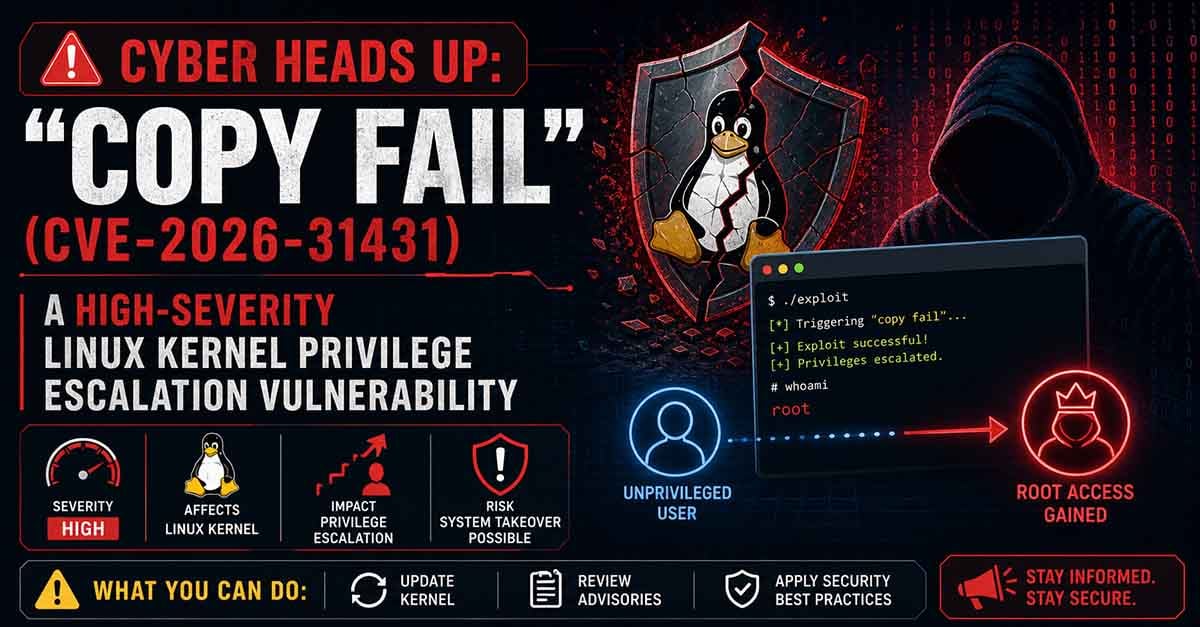
Overview: A high-severity privilege escalation vulnerability has been disclosed in the Linux kernel, tracked as CVE-2026-31431 and nicknamed Copy Fail. The flaw was discovered by Taeyang Lee of Theori and carries a CVSS score of 7.8 (High). A working 732-byte Python proof-of-concept exploit is publicly available, and active exploitation in the wild has been reported.… Continue reading Cyber Heads Up: “Copy Fail” (CVE-2026-31431), a High-Severity Linux Kernel Privilege Escalation Vulnerability
Iranian-U.S./Israeli Hostilities Lead to Increased Threat Landscape
Update, March 15, 2026 Overview: This is an update to the Cyber Heads-up we posted back on March 4, 2026, with detailed information about Iranian threat activity tied to ongoing U.S./Israeli operations. Analysis: At the start of hostilities with Iran, we at Assura took proactive steps to identify and create alerts for known Iranian-sponsored Indicators… Continue reading Iranian-U.S./Israeli Hostilities Lead to Increased Threat Landscape
Updated: ACTIVE EXPLOITATION ALERT: Zero-Day Vulnerability Affecting Self-Hosted SharePoint Servers (CVE-2025-53770/53771)
Updated on 24 July 2025 to add links to external references and add guidance around applying security updates published by Microsoft. Overview: On July 18, 2025, Eye Security identified large-scale exploitation of a zero-day SharePoint vulnerability chain that enables unauthenticated remote code execution (RCE). Within hours, attackers were actively compromising self-hosted SharePoint servers worldwide, deploying… Continue reading Updated: ACTIVE EXPLOITATION ALERT: Zero-Day Vulnerability Affecting Self-Hosted SharePoint Servers (CVE-2025-53770/53771)
Cyber Heads Up: “BadSuccessor”—A Critical Active Directory Privilege Escalation Vulnerability in Windows Server 2025
Overview: Akamai researchers have identified a significant privilege escalation vulnerability in Windows Server 2025, termed “BadSuccessor.” This flaw exploits the newly introduced delegated Managed Service Accounts (dMSAs) feature, allowing attackers to impersonate any Active Directory (AD) user, including domain administrators, without altering existing accounts or group memberships. Key Details: Impact: Exploitation of BadSuccessor can lead… Continue reading Cyber Heads Up: “BadSuccessor”—A Critical Active Directory Privilege Escalation Vulnerability in Windows Server 2025
Cyber Heads Up: Tenable Plugin Update Causes Agents to Disconnect from Cloud Console (Read for Fix)

Overview: We hope you had a fantastic holiday! Unfortunately, the Grinch might have left one last surprise for us – Tenable has identified a critical issue affecting Nessus Agent versions 10.8.0 and 10.8.1, causing some headaches for vulnerability management teams. A recent plugin update has rendered these agents offline and unresponsive, halting vulnerability scans on… Continue reading Cyber Heads Up: Tenable Plugin Update Causes Agents to Disconnect from Cloud Console (Read for Fix)
Phishing Campaign Installs Backdoor-Loaded VM to Evade Antivirus and Harvest Credentials

Overview Assura, Inc. has been made aware of this attack pattern, has taken steps to detect it in our managed services, and is following the attack in the blogs of security researchers who found this campaign. A recent phishing attack campaign has attackers installing a virtual machine (VM) on your Windows system, prebuilt with backdoors… Continue reading Phishing Campaign Installs Backdoor-Loaded VM to Evade Antivirus and Harvest Credentials
CISA Urgent Advisory: Exploitation of Unitronics programmable logic controllers (PLCs)
Overview The Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent advisory concerning the exploitation of Unitronics programmable logic controllers (PLCs) within the Water and Wastewater Systems (WWS) Sector. These critical systems manage various aspects of water treatment and distribution, and cyber threat actors have targeted these PLCs, posing a significant risk to the… Continue reading CISA Urgent Advisory: Exploitation of Unitronics programmable logic controllers (PLCs)