
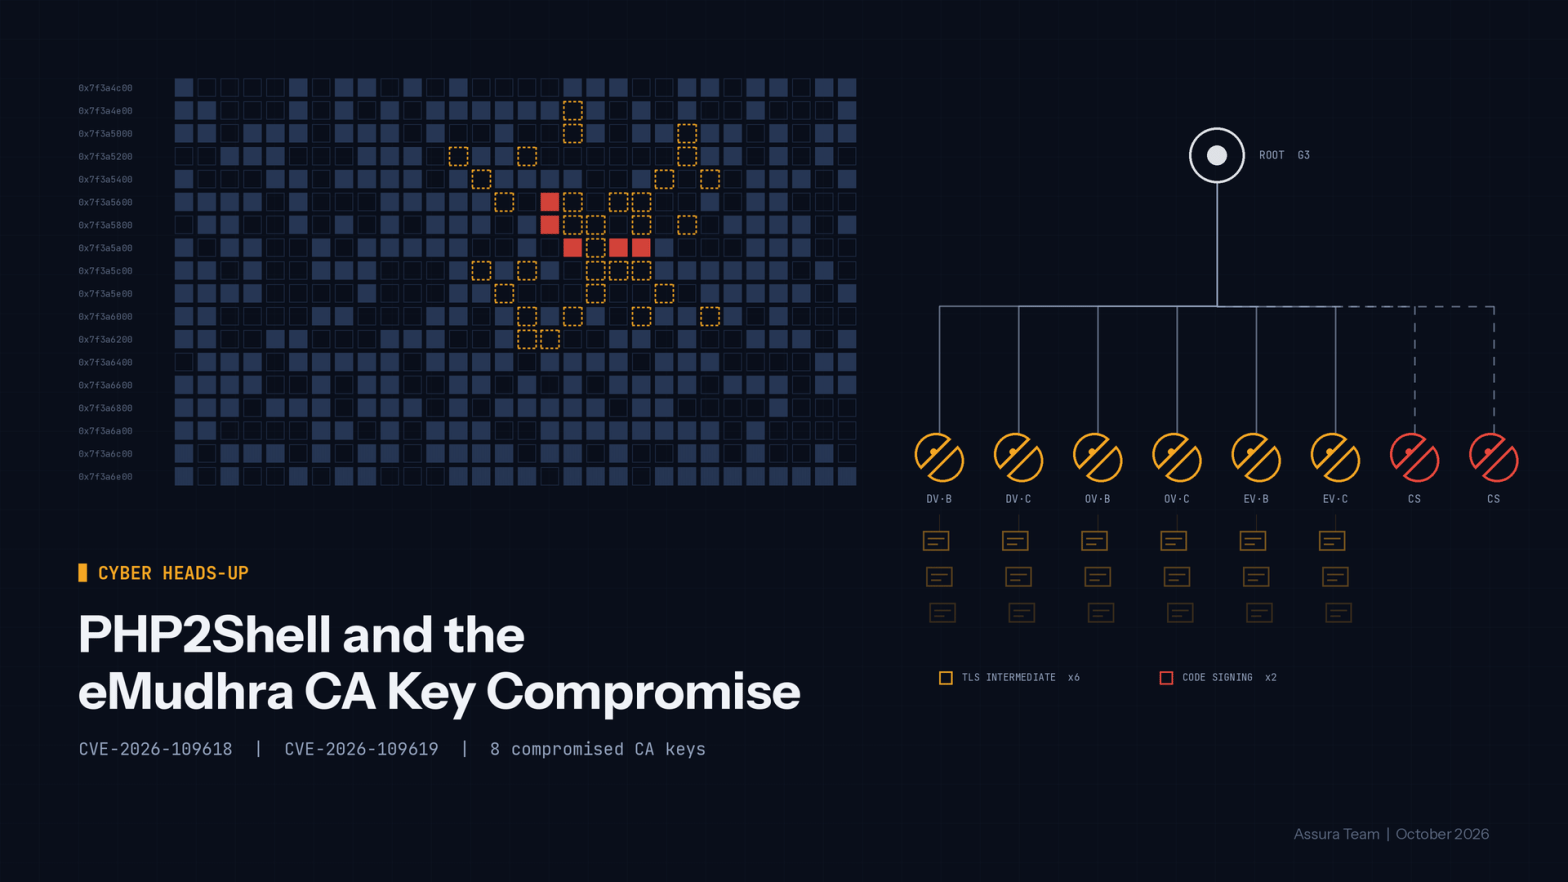
October 20 was a rough day for the internet’s plumbing. Two critical problems surfaced within hours of each other, and both sit in technology nearly every organization runs: the PHP engine behind WordPress, Drupal, Magento, and countless custom applications, and the TLS certificate trust that keeps HTTPS honest. Neither can wait for next month’s maintenance window.
Tag: Cyber Heads Up
Recent Tenable Agent Update Causes False Positives in EDR Software
Good morning, Yesterday (May 25, 2026), the Assura team began receiving reports that various Endpoint Detection and Response (EDR) platforms began quarantining systems running the Tenable Vulnerability Management agent for Windows. Because this is highly unusual, our Security Operations Center (SOC) team conducted a thorough investigation out of an abundance of caution to rule out… Continue reading Recent Tenable Agent Update Causes False Positives in EDR Software
YellowKey BitLocker Bypass and GreenPlasma SYSTEM Escalation Hit Windows 11 and Server 2022/2025
Update, May 26, 2026 Last week, we wrote about YellowKey, the BitLocker bypass that turns a missing Windows 11 laptop into a data exposure event. The proof-of-concept is public, Microsoft has assigned CVE-2026-45585 (CVSS 6.8), and a full security update still has no committed ship date. Mitigation guidance exists, but the choice between Microsoft’s WinRE… Continue reading YellowKey BitLocker Bypass and GreenPlasma SYSTEM Escalation Hit Windows 11 and Server 2022/2025
Iranian-U.S./Israeli Hostilities Lead to Increased Threat Landscape
Update, March 15, 2026 Overview: This is an update to the Cyber Heads-up we posted back on March 4, 2026, with detailed information about Iranian threat activity tied to ongoing U.S./Israeli operations. Analysis: At the start of hostilities with Iran, we at Assura took proactive steps to identify and create alerts for known Iranian-sponsored Indicators… Continue reading Iranian-U.S./Israeli Hostilities Lead to Increased Threat Landscape
UPDATE: Take Immediate Action: Two New Microsoft Exchange Zero-Day Vulnerability confirmed by Microsoft
Overview This Cyber Heads-up has been updated to include a PowerShell command to determine whether an Exchange server has already been compromised. Assura’s Defensive Security Operations Center (SOC) is monitoring recently reported zero-day vulnerabilities in Microsoft Exchange 2013, 2016, and 2019 being exploited in the wild. “The first vulnerability, identified as CVE-2022-41040, is a Server-Side… Continue reading UPDATE: Take Immediate Action: Two New Microsoft Exchange Zero-Day Vulnerability confirmed by Microsoft
Apple announces an ‘actively exploited’ vulnerability that allows hackers to fully control devices
Overview On August 17, 2022, Apple announced a zero-day vulnerability that exploits a software weakness that affects both the kernel (CVE-2022-32894) and the WebKit on Apple devices (CVE-2022-32893). The kernel is a layer of the operating system common on all Apple devices, and the WebKit is part of the default Apple web browser, Safari. Apple… Continue reading Apple announces an ‘actively exploited’ vulnerability that allows hackers to fully control devices
Follina Zero-day Exploit Permits Attackers Complete Takeover of Victim Systems Through Malicious Microsoft Office Documents
Overview of Follina On Friday, May 27th, 2022, @nao_sec announced on Twitter that they had discovered a novel attack technique utilized in a malicious document (maldoc) submitted from a Belarus IP address to VirusTotal. The new technique uses Microsoft’s Microsoft Support Diagnostic Tool (MSDT) to retrieve and execute malicious code from a remote URL. Microsoft… Continue reading Follina Zero-day Exploit Permits Attackers Complete Takeover of Victim Systems Through Malicious Microsoft Office Documents
CISA Releases Advisory About Multifactor Authentication Bypass with Duo — Duo Responds
TL;DR Russian state-sponsored attackers compromised an NGO by exploiting the weak credentials of an inactive user, default settings in the Duo multifactor authentication service, and PrintNightmare to take over the environment. The way to protect organizations is to implement good cyber hygiene and modifying a couple of default settings in Duo. Overview On Tuesday, March… Continue reading CISA Releases Advisory About Multifactor Authentication Bypass with Duo — Duo Responds
UPDATE: NVIDIA Code Signing Certificates Compromised – Temporarily Halt Updates/Installation of NVIDIA Software
Update March 16, 2022: It’s been twelve days since we posted this Cyber Heads-up and this seems to have dropped out of the news and out of discussion. NVIDIA has been deafeningly silent about this. Our guidance remains the same. Make sure that your environment is set up to monitor for code signed by these… Continue reading UPDATE: NVIDIA Code Signing Certificates Compromised – Temporarily Halt Updates/Installation of NVIDIA Software
Assura Continues to Recommend Operation in a “Shields Up” Defensive Posture
TL;DR Earlier in February, the Cybersecurity and Infrastructure Security Agency (CISA) issued a “Shields Up” warning advising American companies to be extra cautious about potential hacking attempts from Russia as tensions with the country rise, particularly during the Russia-Ukraine crisis. As the situation since the invasion of Ukraine by Russia on Thursday, February 24th continues to evolve, Assura… Continue reading Assura Continues to Recommend Operation in a “Shields Up” Defensive Posture