
Your scanner found thousands of vulnerabilities.
Now what?
We turn that list into a program.
Assura’s Vulnerability Management-as-a-Service pairs expert analysis with automated remediation workflows so you know what to fix first, who is fixing it, and whether it actually got closed. Since 2007, we have helped organizations stop drowning in findings and start reducing real risk.
A scan is not a program.
Every vulnerability scanner produces findings. Thousands of them, scored by a formula that does not know which systems your business actually depends on, which vulnerabilities attackers are actively exploiting right now, or which ones your team can realistically patch this month. So the list grows. Tickets get opened and ignored. Critical findings sit unresolved for months because nobody owns them and nobody is tracking whether they close.
That is not a vulnerability management program. That is a vulnerability management problem.
What a real program covers.
We assess your infrastructure, your applications, or both, using your existing scanners or ours. Then we do what the scanner cannot: we tell you what actually matters and make sure it gets fixed.
Infrastructure and OT
Real-world vulnerability assessment across your network, endpoints, servers, and operational technology. We can provide Tenable Vulnerability Management through Assura, or work with your existing Rapid7 InsightVM, Qualys, or other scanner.
- External and internal network scanning
- Server, endpoint, and cloud infrastructure
- Operational technology and ICS environments
- Misconfiguration and exposure identification
Web Application and API
Vulnerability assessment for the applications your business runs and ships. Works with your existing Snyk, Veracode, Acunetix, or other application security scanner.
- Web application vulnerability scanning
- API security assessment
- Software composition analysis
- Integration with your existing AppSec toolchain
Expert Analysis and Prioritization
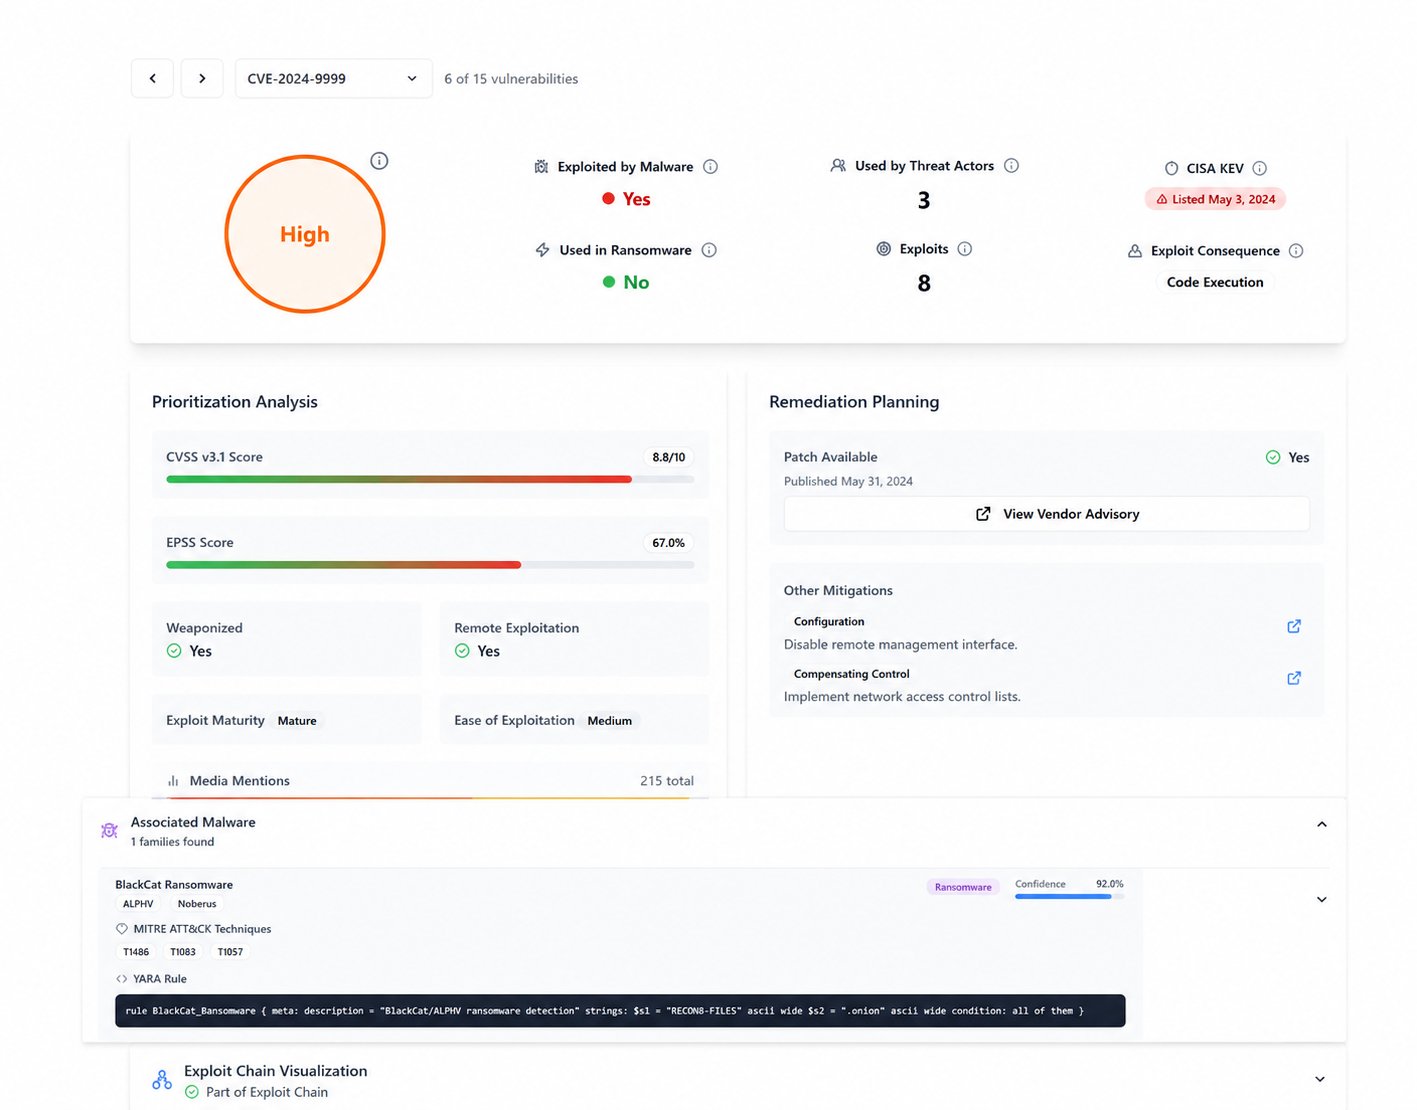
A scanner score is not a remediation plan. Our analysts review findings in the context of your environment, your business, and current threat intelligence to tell you which vulnerabilities to fix first and why.
- Risk-based prioritization beyond CVSS scores
- Threat intelligence correlation including CISA KEV and active exploit data
- Business context applied to asset criticality
- Clear, actionable guidance for your remediation teams
Remediation Workflow and Reporting
Knowing what to fix is only half the problem. We use Nucleus to automate ticket routing to the right teams, track remediation status, enforce SLAs, and give you the dashboards and reports your board and your auditors need.
- Automated ticket creation and ownership assignment
- SLA tracking and remediation status management
- Executive dashboards and trend reporting
- Compliance-ready documentation
Aligned to the frameworks you answer to:
How the program runs.
Every engagement follows the same four-phase cycle, repeated continuously so your exposure shrinks over time rather than compounding.
Discover
Know what you have.
You cannot manage what you cannot see.
- Authenticated scanning across your infrastructure and application assets
- Asset discovery and inventory reconciliation
- Coverage verification to eliminate blind spots
- Baseline established for trend tracking over time
Verify
Confirm what is real.
Not every finding is a real risk. We validate exploitability before you spend a single hour on remediation.
- Analyst review of scanner output to eliminate false positives
- Exploitability assessment using current threat intelligence
- CISA KEV and active exploit correlation
- Severity re-rated in the context of your actual environment
Prioritize
Fix the right things first.
We rank findings by what an attacker would actually use against you, not by what the scanner scored highest.
- Risk-based ranking incorporating asset criticality and business impact
- Remediation plan delivered with clear ownership assignments
- SLA targets set by severity so nothing critical lingers
- Your team knows exactly what to work on this week
Remediate
Close the loop.
We run the program. Your teams do the patching. Nucleus makes sure nothing falls through the cracks.
- Automated ticket routing to the right owners via Nucleus
- Status tracking and SLA enforcement across all open findings
- Retesting to verify findings are actually closed, not just marked closed
- Continuous reporting so progress is always visible
Who runs this program with us.
Vulnerability management lands differently depending on where you sit in the organization.
For the leader who inherited security.
Security landed on your plate along with a scanner that produces a report nobody acts on. You need someone to tell you which vulnerabilities actually matter, get the right people to fix them, and give you something to show leadership when they ask how the program is going. That is exactly what we do. If you are also responsible for the applications your organization buys or builds, we can cover those too.
For the security leader building a program.
You know what a mature vulnerability management program looks like. You need the operational infrastructure to run one without hiring a team to do it. We bring the expert analysis, the Nucleus platform, and the program management so you can focus on strategy and stakeholder communication while we handle execution. Our reporting gives you the board-ready metrics and trend data to show the program is working.
Why teams choose Assura for vulnerability management.
We prioritize by risk, not by CVSS score.
CVSS scores do not know your environment. A critical-rated vulnerability on an air-gapped system that holds no sensitive data is not your most urgent problem. A medium-rated vulnerability on your customer-facing payment infrastructure with a public exploit available absolutely is. Our analysts make that call for you, every cycle.
The right people fix it, automatically.
Knowing what to fix means nothing if the ticket goes to the wrong team and sits. We use Nucleus to automatically route remediation work to the right owners based on asset type, team, and severity. SLAs are tracked. Nothing critical ages past its deadline without someone being accountable.
Your scanner, or ours.
You may already have Tenable, Rapid7, Qualys, Snyk, or another scanner you have invested in. We work with it. If you need scanning capability, we can provide Tenable Vulnerability Management as part of the program. Either way, everything feeds into one platform and one program.
Tested to the standard you answer to.
When we scope a vulnerability management program to meet a regulatory or contractual requirement, we stand behind it. If your assessor or auditor finds that our work does not satisfy that requirement, we fix it at our expense, no matter the cost. That’s the AuditArmor® Guarantee.
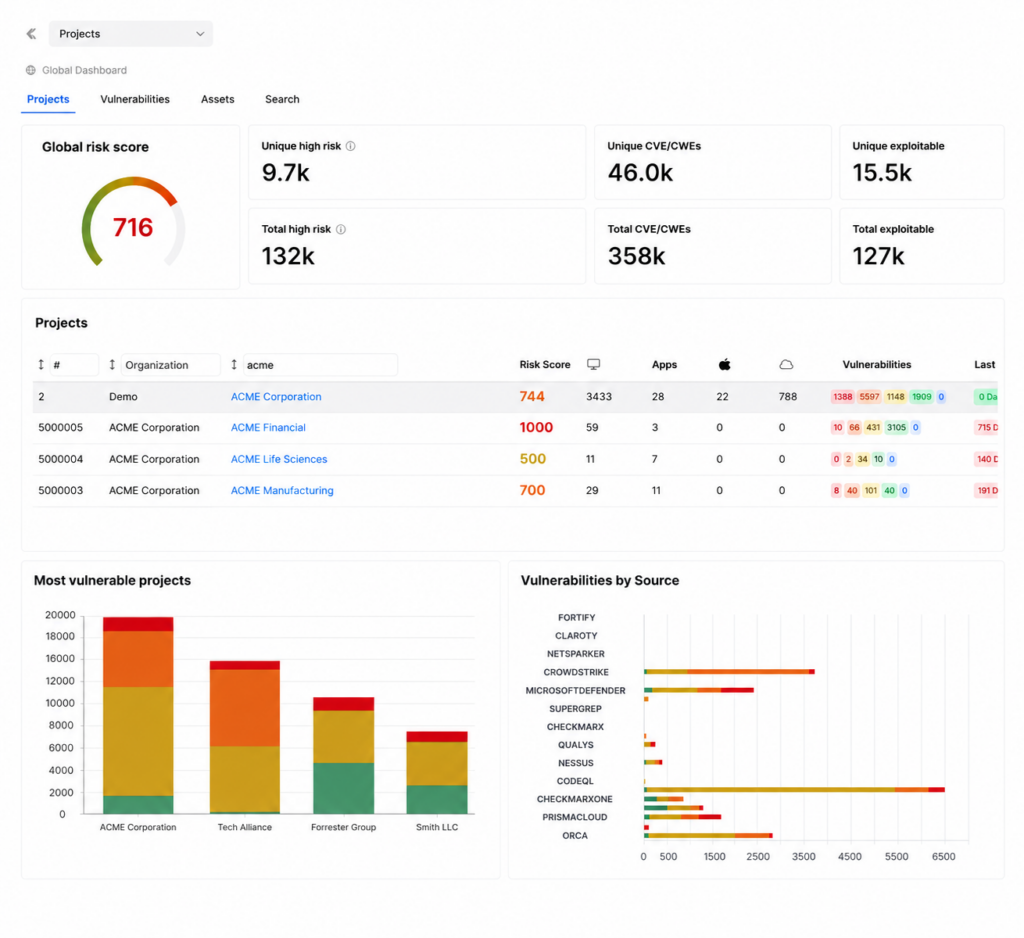
Your results, live and always current.
Every finding, every owner, every remediation deadline, and every trend line, visible in one place. Your executives get the dashboard. Your auditors get the report. Your remediation teams get the ticket. Nobody has to manage a spreadsheet. And if your organization runs our Managed SIEM/XDR service, vulnerability findings from Tenable, Rapid7, Qualys, or other connected scanners feed directly into the Stellar Cyber platform, so your SOC can correlate active vulnerabilities with live threat activity in a single view.
Proven where it counts.
In just three months, we reduced our critical and high vulnerabilities from over 4,000, which were significantly past our internal SLAs, to fewer than 100. We could not have achieved this without Assura’s risk-based approach and guidance. They make vulnerability management and patching manageable.
IT Director, Regional Medical Practice
48185
CVEs published in 2025 alone
24%
Average annual growth in published CVEs since 2022
31%
of breaches began with an exploited vulnerability, now attackers' top way in (Verizon 2026 DBIR)
Infrastructure assets, application assets, or both.
Most clients start with infrastructure and expand to applications as their program matures. The service is the same either way: expert-led, Nucleus-powered, and scoped to the assets you need covered.
Infrastructure Asset Coverage
Networks, servers, endpoints, OT
Continuous vulnerability assessment and managed remediation workflows for your infrastructure environment. Includes expert prioritization, remediation guidance, Nucleus-powered ticket routing and SLA tracking, and executive reporting. Scanner options available.
Application Asset Coverage
Web apps, APIs, custom software
Vulnerability assessment and managed remediation workflows for your web applications and APIs. Works with your existing AppSec scanner or we can recommend one. Same expert prioritization, remediation guidance, and Nucleus-powered workflow as infrastructure coverage.
Many clients run both. If you are not sure where to start, infrastructure coverage is the right first step for organizations that don’t develop their own custom applications.
Stop managing a list. Start running a program.
Let us scope a vulnerability management program to your environment, your scanners, and your compliance requirements. You will walk away knowing exactly what you have, what matters, and what is being done about it.
Frequently Asked Questions
What does Assura's Vulnerability Management-as-a-Service include?
Assura's VMaaS covers infrastructure and OT vulnerability assessment, web application and API scanning, expert risk-based prioritization, and automated remediation workflow management using Nucleus. It works with your existing scanners (Tenable, Rapid7, Qualys, Snyk) or provides Tenable Vulnerability Management as part of the program.
How is Assura's vulnerability prioritization different from CVSS scores?
CVSS scores do not account for your specific environment. Assura's analysts apply business context, asset criticality, and current threat intelligence including CISA KEV and active exploit data to prioritize findings by real risk. A medium-rated vulnerability on a customer-facing payment system with a public exploit available takes precedence over a critical-rated vulnerability on an air-gapped system with no sensitive data.
How does Assura track and manage remediation?
Assura uses Nucleus to automatically route remediation tickets to the right teams based on asset type, team, and severity. SLAs are tracked, dashboards give executives and auditors the reporting they need, and nothing critical ages past its deadline without accountability. Your board gets the dashboard, your auditors get the report, and your remediation teams get the ticket.
Can Assura work with my existing vulnerability scanner?
Yes. Assura works with Tenable, Rapid7 InsightVM, Qualys, Snyk, Veracode, Acunetix, and other scanners you have already invested in. If you need scanning capability, Assura can provide Tenable Vulnerability Management as part of the program. Either way, all findings feed into one platform and one program.
Does Assura's vulnerability management satisfy compliance requirements?
Yes. Assura scopes vulnerability management programs to meet specific regulatory and contractual requirements including PCI DSS, HIPAA/HITECH, CMMC, SOC 2, NIST SP 800-53, and others. If your assessor or auditor finds that Assura's work does not satisfy that requirement, Assura fixes it at its own expense under the AuditArmor® Guarantee.
How does VMaaS integrate with Assura's Managed SIEM/XDR service?
If your organization runs Assura's Managed SIEM/XDR service, vulnerability findings from Tenable, Rapid7, Qualys, and other connected scanners feed directly into the Stellar Cyber platform. Your SOC can then correlate active vulnerabilities with live threat activity in a single view, closing the loop between vulnerability management and detection and response.