
Your inbox is the most targeted surface in cybersecurity. We guard it around the clock.
Powered by IRONSCALES and Assura’s Security Operations Center, our managed email security service stops phishing, business email compromise, account takeover, and AI-generated threats before they reach your people.
Your email filter is not enough anymore.
Generative AI has fundamentally changed the economics of phishing. Attacks that once took hours to craft now arrive by the thousands, personalized, convincing, and purpose-built to bypass the tools most organizations already have in place.
Four layers of protection working as one.

Mailbox-Level BEC Detection
AI analyzes each mailbox individually to detect impersonation, display name spoofing, vendor email compromise, and account takeover attempts before they land.

AI-Powered Incident Response
Threats flagged by users or detected by the platform are investigated and remediated automatically. Assura’s analysts handle the judgment calls that require human decision-making.

Crowdsourced Threat Intelligence
Every client environment feeds a shared defense network. A threat neutralized at one organization is blocked across all of them in real time.

Account Takeover Protection
IRONSCALES detects the behavioral signals that indicate a compromised mailbox, even when credentials are valid, and alerts Assura’s SOC for immediate response.
Relevant compliance frameworks
CMMCCJISFFIECGLBAHIPAA/HITECHHITRUST CSFIRS 1075ISO 27001/27002NIST CSFNIST SP 800-53NIST SP 800-171PCI DSSSOC 2
Who this service is built for.
For the leader who inherited security.
Email security fell into your lap along with everything else. You do not have a dedicated analyst watching your inbox, and you know your current filter is missing things. You need a solution that works without requiring you to become an email security expert.
And when auditors ask about email controls, you need to be able to show them something real.
For the executive accountable for outcomes.
Your organization handles sensitive data, operates under regulatory requirements, or both. A phishing attack that succeeds is not just an IT problem. It is a business problem, a compliance problem, and potentially a career problem.
You need email protection that holds up under audit scrutiny and gives you something credible to report to the board.
Already running a mature security program? Email security telemetry from IRONSCALES feeds directly into your SOC or ours service, so phishing signals from your inbox are correlated against endpoint and network activity in our SOC.
Why Assura's managed email security is different.
Human analysts, not just automation
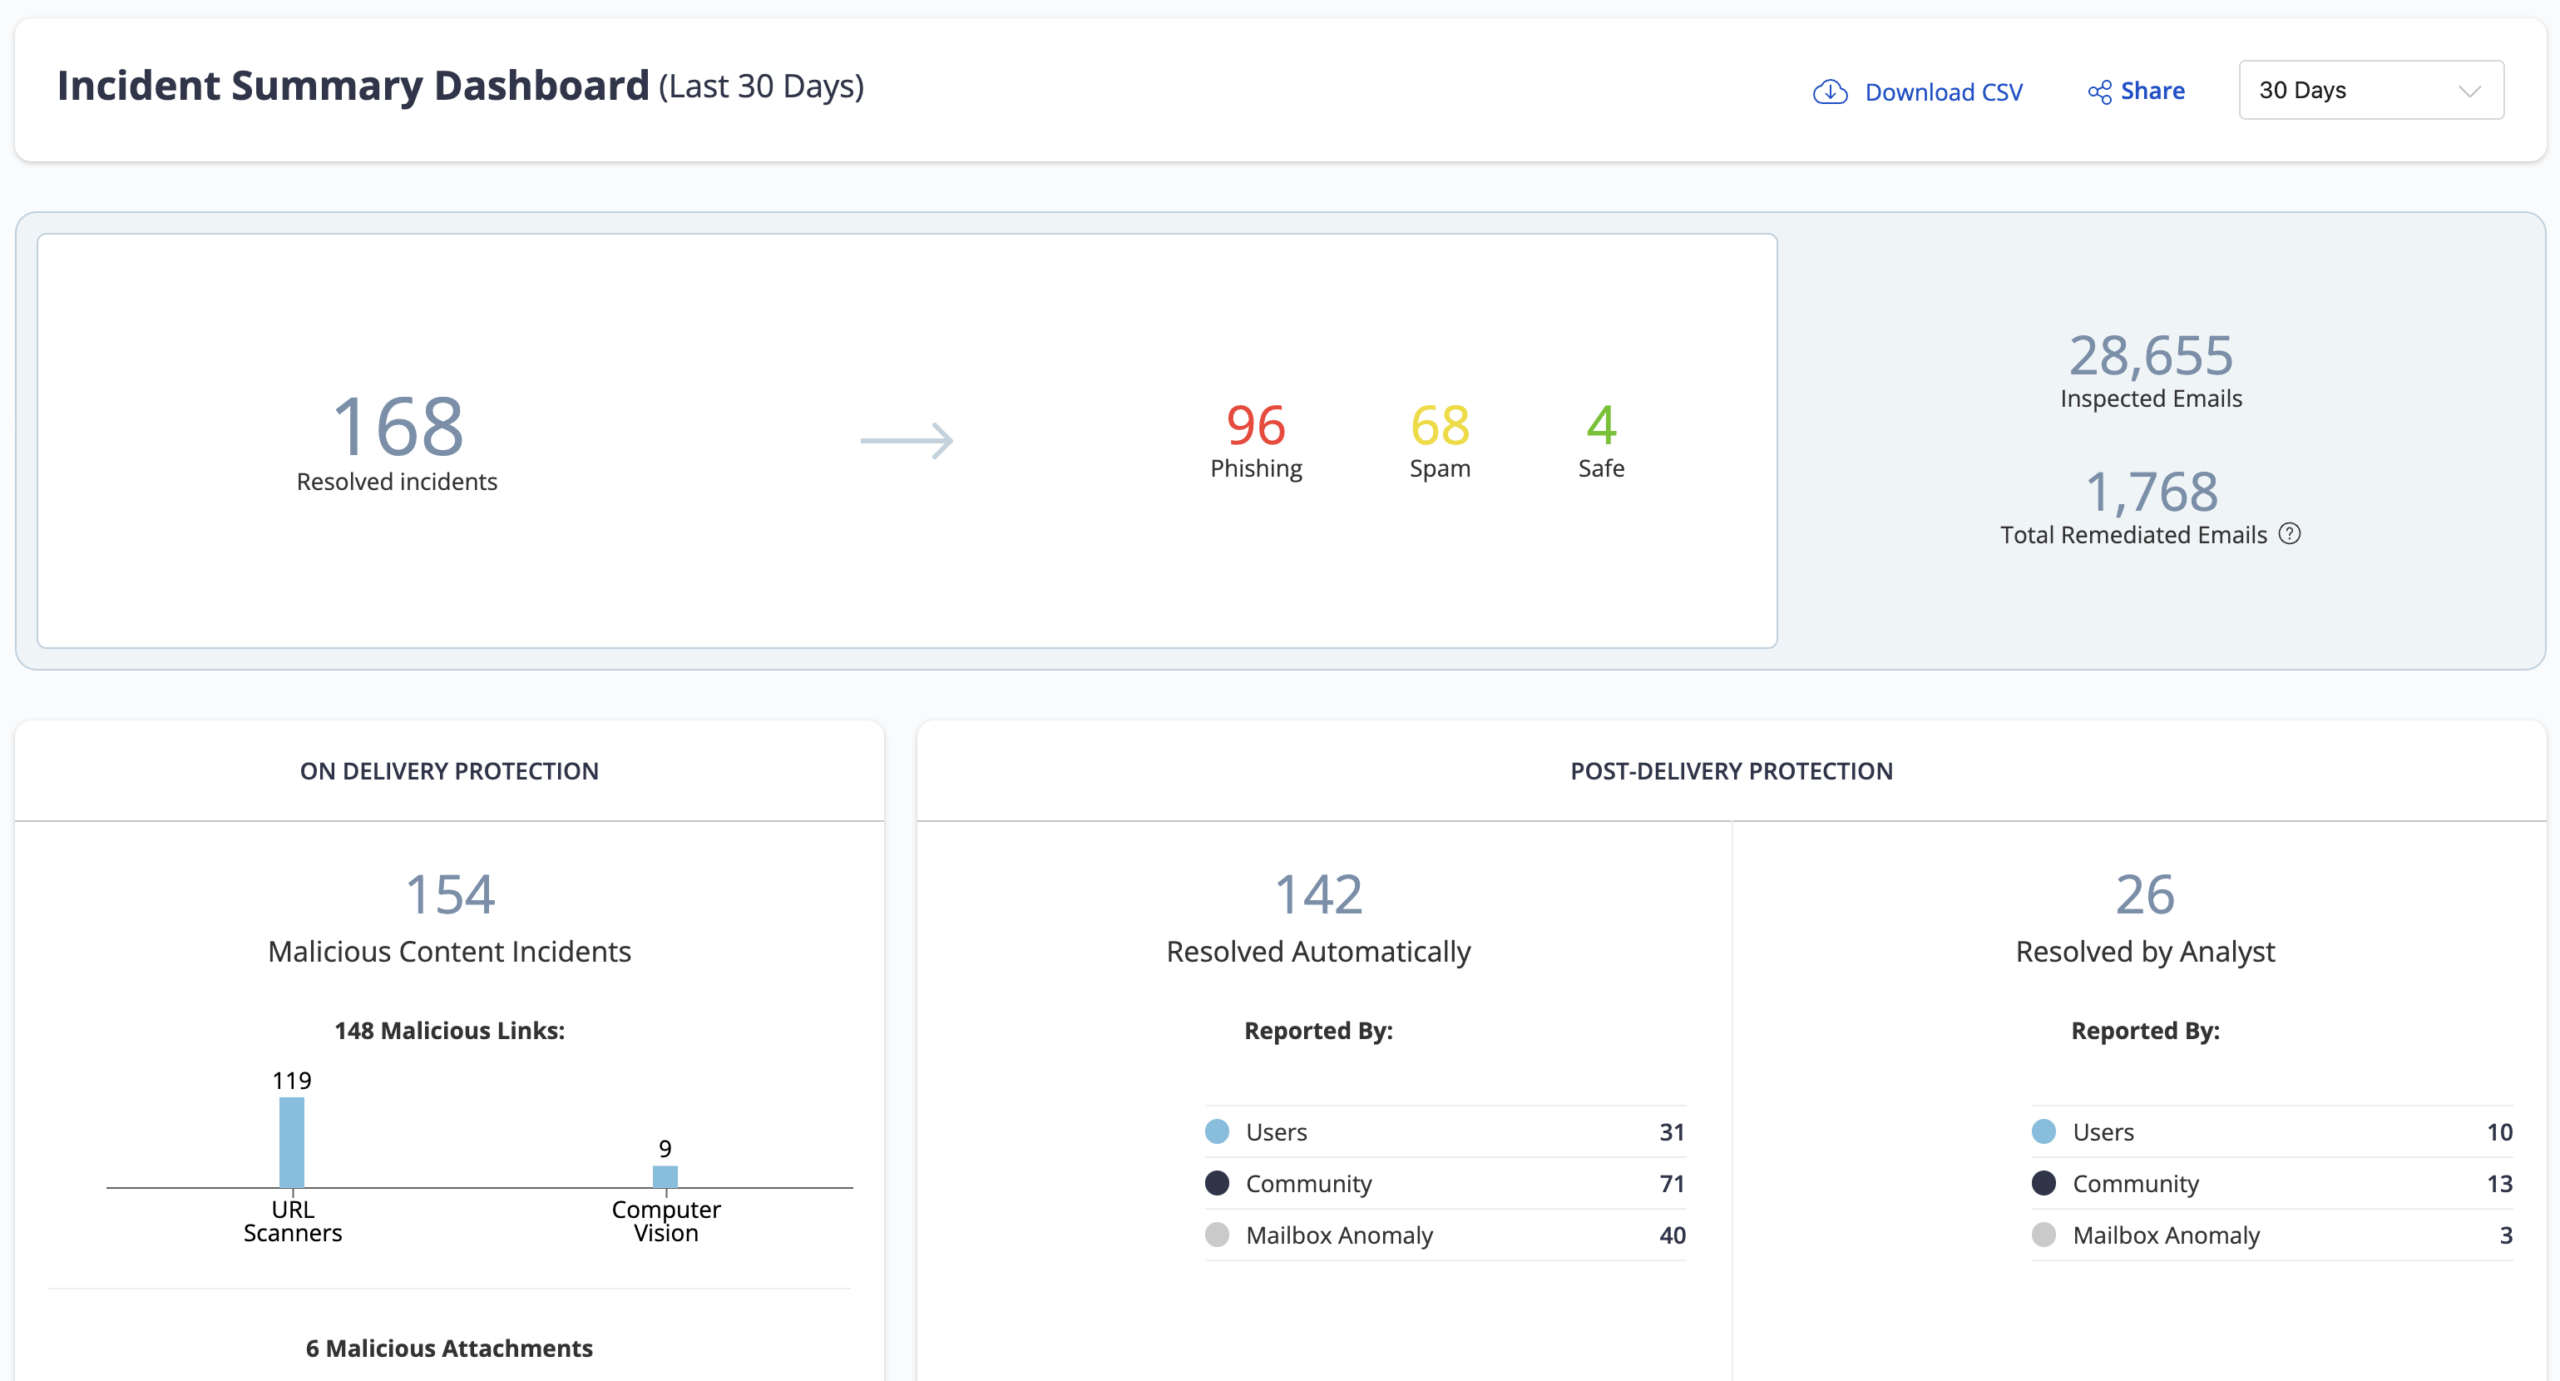
IRONSCALES resolves the majority of incidents automatically. Assura’s SOC handles the ones that require a human decision. You get both layers, not one or the other.
API-native, not a gateway
IRONSCALES deploys via API directly into Microsoft 365 or Google Workspace. No MX record changes, no mail routing delays, and no disruption to your existing mail flow.
Telemetry that feeds your whole program
Phishing signals from your email environment flow directly into our Managed SIEM/XDR service, so Assura’s SOC can correlate email-borne threats with endpoint and network activity in a single view.
Backed by the AuditArmor® Guarantee
If you follow our recommendations and your audit reveals a compliance variance in work Assura performed, we fix it at our expense.
The IRONSCALES platform
IRONSCALES combines adaptive AI, mailbox-level behavioral analysis, and a crowdsourced threat network to detect and remediate email threats that traditional secure email gateways miss. The platform operates at the mailbox level, which means it sees every message after delivery and can retroactively remove threats already in the inbox.
Assura’s SOC monitors the platform continuously, tunes detection policies for your environment, and escalates incidents that require analyst judgment. Phishing telemetry from IRONSCALES also feeds into the Managed SIEM/XDR platform, giving our analysts correlated visibility across email, endpoint, and network layers.
Phishing attempts that would have reached our people are now getting stopped before anyone ever sees them, despite having an email security gateway in place. That’s exactly what we needed.
VP of IT, Regional Hospital
1:04
Median incident resolution time (vs. 27.5-minute industry median)
84
Percent of threats resolved automatically, without analyst intervention
#94
Top 250 MSSP globally
Choose the coverage model that fits your organization.
Essential Protection
- IRONSCALES platform (BEC, ATO, malware, and URL protection)
- AI-powered automated remediation
- Crowdsourced threat intelligence network
- Assura SOC monitoring and escalation
- Monthly reporting
Advanced Coverage
- Everything in Essential Protection
- Priority Assura analyst response
- Deep-dive monthly threat briefings
- Compliance evidence package (audit-ready reports)
- DMARC management: Stops attackers from sending email that appears to come from your domain.
Pair this service with Security Awareness and Training to address both the technical and human sides of your email threat exposure.
Stop treating email security like a problem for later.
Every day without managed email security is a day a well-crafted phishing attempt can land. Let’s talk about what it takes to protect your organization.
Frequently Asked Questions
What is the difference between a Secure Email Gateway and what IRONSCALES does?
A Secure Email Gateway sits in front of your mail server and filters messages before they are delivered. It is good at blocking known threats: spam, malware, and phishing emails that match signatures in its database. What it cannot do well is detect threats it has not seen before, including the personalized, AI-generated phishing emails that now arrive without the telltale signs that traditional filters catch.
IRONSCALES deploys via API directly into your Microsoft 365 or Google Workspace mailbox, after delivery. It also remediates retroactively, pulling a threat from every inbox across your organization after it has been identified, even if it was already delivered. It analyzes every mailbox individually, learns what normal communication looks like for each user, and detects anomalies that a gateway would miss: display name spoofing, impersonation of trusted contacts, vendor email compromise, and account takeover attempts.
The two are not mutually exclusive. Many organizations run both, and IRONSCALES works alongside your existing gateway rather than replacing it.
Does managed email security work with both Microsoft 365 and Google Workspace?
Yes. IRONSCALES deploys via API into both Microsoft 365 and Google Workspace. There are no MX record changes, no mail routing adjustments, and no disruption to your existing mail flow. Deployment is non-disruptive by design, which means your users notice nothing during onboarding and your email continues to flow normally from day one.
Does this service work with on-premises Exchange?
IRONSCALES supports on-premises Exchange environments, but Assura's managed email security service does not. We support Microsoft 365 and Google Workspace only. If your organization is running on-premises Exchange and considering a move to Microsoft 365, that transition would make you eligible for this service. We are happy to discuss that path as part of a broader engagement.
What is Business Email Compromise and why is it hard to detect?
Business Email Compromise (BEC) is a category of attack in which a threat actor impersonates a trusted person, typically an executive, a vendor, or a financial contact, to trick an employee into taking a harmful action: wiring money, changing payment details, sharing credentials, or disclosing sensitive information. No malware is involved. The email often contains no links or attachments. It is just a convincing message from someone who appears to be who they say they are.
That is exactly what makes it hard to detect. Traditional email filters look for malicious payloads, suspicious links, and known bad domains. A well-crafted BEC email has none of those. It passes every technical filter because technically there is nothing wrong with it. The threat is entirely in the social engineering: the right name, the right tone, the right context, arriving at the right moment.
IRONSCALES addresses this at the mailbox level, learning each user's normal communication patterns and flagging messages that deviate from them, even when the email itself looks clean. That is the detection layer that a gateway cannot provide.
What is account takeover and how does IRONSCALES detect it?
Account takeover (ATO) occurs when an attacker gains access to a legitimate user's email account, typically through stolen credentials, and uses it to send attacks from inside your organization. Because the emails come from a real, trusted account rather than an external impersonator, they bypass most security controls and are far more convincing to recipients.
IRONSCALES detects account takeover by monitoring the behavioral signals that indicate a compromised mailbox, even when the credentials used to access it are valid. Unusual sending patterns, atypical login locations, unfamiliar devices, and communication behavior that deviates from the user's established baseline all trigger alerts. When IRONSCALES flags a potential account takeover, Assura's SOC investigates and responds immediately.
What is DMARC and why does it matter?
DMARC (Domain-based Message Authentication, Reporting, and Conformance) is an email authentication protocol that tells receiving mail servers what to do with messages that claim to come from your domain but fail authentication checks. Without DMARC, an attacker can send emails that appear to come from your domain, targeting your customers, partners, or employees with phishing attacks that carry your organization's name and brand.
Implementing DMARC at enforcement stops that. It instructs receiving servers to reject or quarantine messages that fail authentication, so your domain cannot be spoofed to attack others.
DMARC management is included in Assura's Advanced Coverage tier. We configure and maintain your DMARC record, monitor authentication reports, and move you to enforcement in a controlled way that does not disrupt legitimate mail flow, which is where most self-managed DMARC implementations stall.
Does this service protect against attacks delivered through Microsoft Teams?
Yes. IRONSCALES offers protection against phishing and social engineering attacks delivered through Microsoft Teams, not just email. As attackers increasingly use collaboration platforms to bypass email security controls, Teams has become a meaningful attack surface, particularly for organizations that allow external message requests from outside their tenant.
Assura's managed service includes Teams protection when it is enabled as part of your IRONSCALES plan. If your organization uses Teams extensively or allows external collaboration, this is worth discussing during the scoping conversation.