
Hack yourself first.
Find your gaps.
Fix what attackers would exploit.
Scanners flag noise. Attackers find paths.
Exploitable, not just noisy.
Network and Infrastructure
Real-world exploits against your perimeter and your internal controls, with every finding validated rather than just scanned.- External network penetration testing
- Internal network penetration testing
- Wireless and Wi-Fi network testing
Applications, Cloud, and AI
Deep assessment of the software, services, and AI systems your business runs on and sells.- Web application and API testing
- Cloud configuration and identity testing across platforms such as AWS, Azure, and GCP
- GenAI and agentic AI testing
Operational Technology
Testing for the industrial and control systems that run physical operations, where safety and uptime matter as much as data.- ICS and SCADA assessment
- PLC and field device testing
- IT and OT segmentation validation
People and Physical
Your people and your facilities are part of your attack surface. We test both.- Social engineering: phishing, vishing, USB drops, and in-person pretexting
- Physical security assessment
Aligned to the frameworks you answer to:
How an engagement works.
Before anyone touches a system, we agree on exactly what we are testing and why. Here is how a full engagement unfolds.
Before
We scope it to you.
Your objectives defined up front, locked into a signed Rules of Engagement before we start.
- Objective defined up front: maximum exploitable findings, a specific target, access to sensitive data, or whether your team detects and responds
- Hands-on human testing tailored to your environment, not a tool scan
- Scope, authorized targets, test windows, and contacts locked in a signed Rules of Engagement
During
Real attacks, validated findings.
Our testers work inside the agreed rules, using the same techniques a real attacker would.
- Execution against recognized frameworks: NIST SP 800-115, OWASP, OSSTMM, and PTES
- Every finding validated for exploitability and rated from Informational to Critical
- Anything Critical, or any sign of a real intruder, reported to you immediately, not at the end
After
A plan, not a data dump.
You leave with clear next steps and briefings for both your executives and your technical team.
- Prioritized report with executive summary, technical findings, and step-by-step reproduction
- Sixty calendar days to retest any finding at no extra charge
- Results available in the reporting portal for a full year
Who we test for.
For the security leader.
You know security, and you are maturing a program with limited resources. You need to know your defenses hold up against a real attacker, not just a checklist. Our validated, business-impact-ranked findings tell you exactly where to spend next, and we can test whether the detection and response you are building actually fires. You walk away with evidence you can take to your board.For the leader who inherited security.
Security landed on your plate, and you have got tools and maybe an outside SOC, but no real proof any of it works. An outside test shows you whether your defenses, and the people and tooling meant to catch an intruder, actually hold up. You get a plain-English walkthrough of how an attacker would move and a prioritized plan you can act on, without having to be a pen testing expert yourself.Why teams choose Assura.
Real testers, not just tools.
Scanners have their place, but they do not think like an attacker. Our engagements are hands-on, human-led testing where our testers build custom exploits against your actual environment, drawing on the experience we have earned since 2007. Automated tools are a starting point, not the test.We test your defenders, not just your defenses.
Finding the hole is only half the picture. The other half is whether anyone notices. We can run engagements that deliberately probe whether your monitoring, your SOC, or your outside provider actually detects and responds to a real intrusion. If we get in and out and no one caught us, that is a finding in itself, and a good reason to talk about ProDefense, our managed detection and response.Findings you can reproduce and learn from.
Every finding comes with step-by-step reproduction instructions and a plain-English attack narrative showing how separate issues chain into a real breach. Your team gets tailored guidance, not just a severity score, so the test leaves you measurably stronger rather than just informed.Tested to the standard you answer to.
When we scope a penetration test to meet a regulatory or contractual requirement, we stand behind it. If your assessor or auditor finds the test we delivered does not satisfy that requirement, we fix it at our expense, no matter the cost. That is the AuditArmor® Guarantee.Your results, live and trackable.
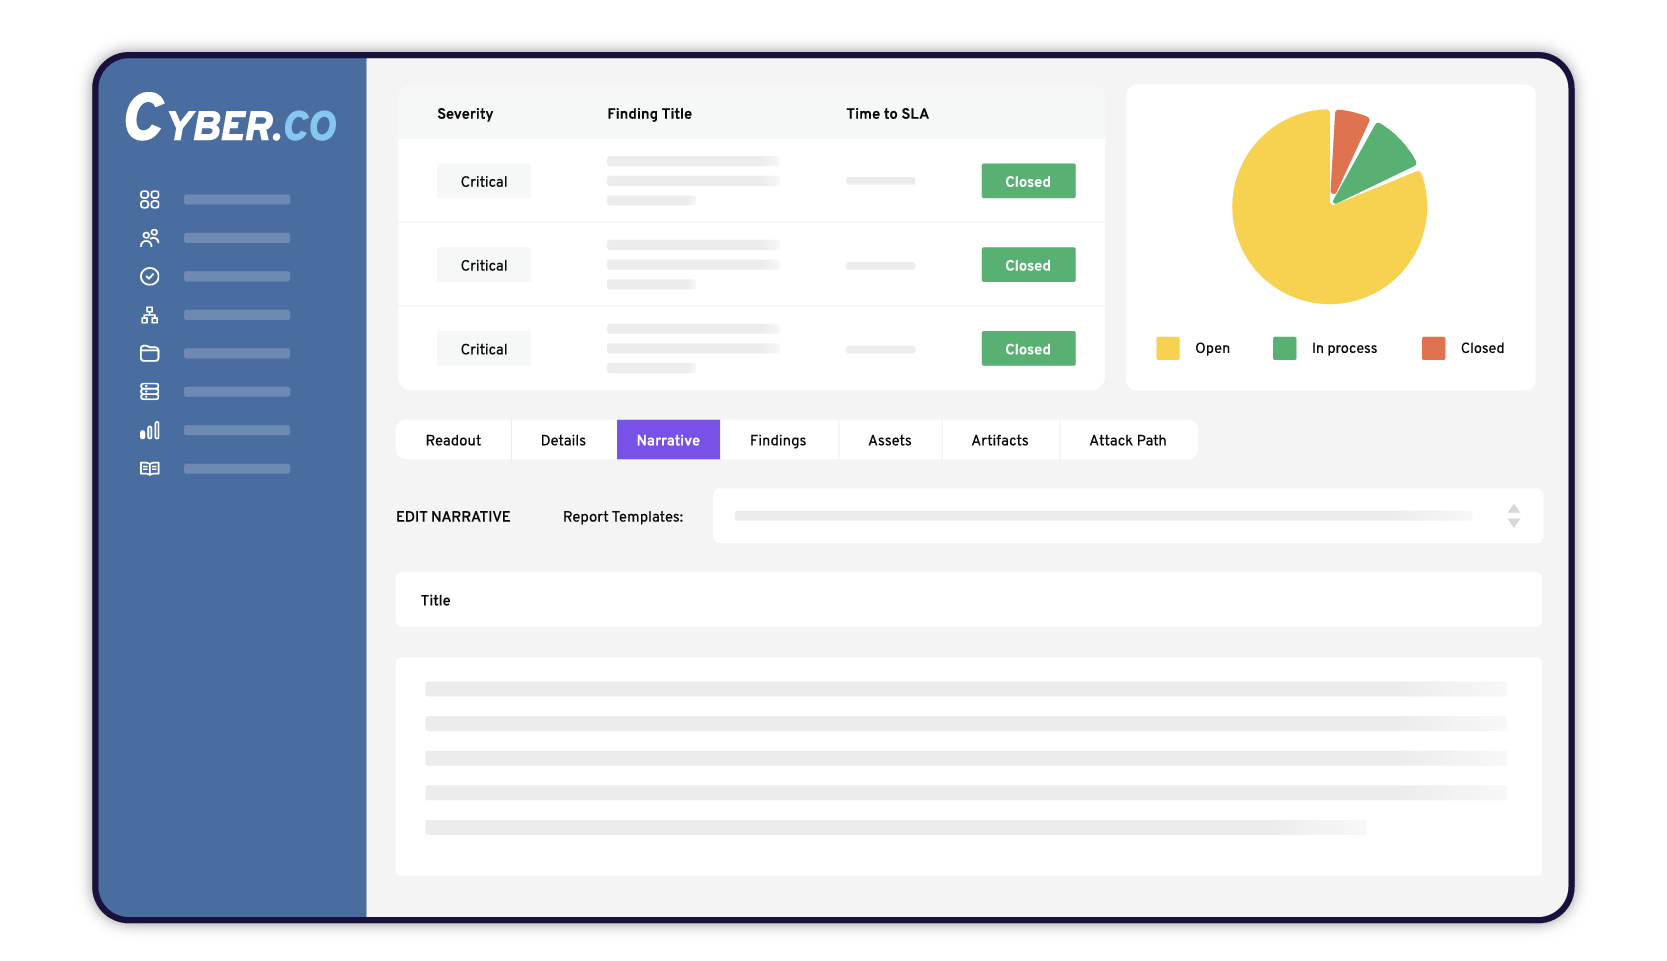
Proven where it counts.
I think that that’s one of the like, kudos I will give Assura, is your pen test reports are so detailed that they help me to be able to figure out how would I test this on my own and make sure I’ve fixed it. You obviously do the retests, but like, then the year after we might stand up another, you know, server and we need to harden that. We need to make sure that that’s not vulnerable to the same problem. So like, I’ve gone back to old Assura pen tests and been like, how did they do that?
Information Security Manager for a Regional Healthcare Provider
19
Years of hands-on testing experience
60
Days of retesting included at no extra charge
#94
Top 250 MSSP, 2025
Building a startup and selling to enterprise customers?
Start with the AppSec Vibe Check.
The AppSec Vibe Check gives you a fast, credible read on whether the software you sell is secure enough for enterprise buyers, ideal before a funding round or a major sales conversation. A clean SOC 2 audit also means testing the environment behind your product, so an infrastructure penetration test is the natural next step, and we will scope it with you when you are ready.One test, or a recurring program.
Time-Boxed Penetration Test
On demand or annual
A scoped engagement with a defined start and end. Ideal for an annual requirement, a point-in-time validation, or a first look at how we work. You get the full methodology, validated findings, access to the reporting portal, and sixty days of retesting at no extra charge.Penetration Testing-as-a-Service
Recurring testing
Deeper, broader coverage than any single test window can deliver, built for evolving environments and applications. We test on a recurring cadence, so the gaps that open up between annual tests are caught before an attacker can exploit them. We recommend a monthly cadence for the strongest results, with a quarterly option available when budget calls for it.Find your gaps before an attacker does.
Frequently Asked Questions
What types of penetration testing does Assura offer?
Assura offers network and infrastructure testing (external, internal, and wireless), web application and API testing, cloud configuration testing across AWS, Azure, and GCP, GenAI and agentic AI testing, operational technology and ICS/SCADA testing, and social engineering and physical security assessments.
How is Assura's penetration testing different from running a vulnerability scanner?
Scanners identify potential vulnerabilities but cannot validate whether they are actually exploitable. Assura's testers build custom exploits against your real environment, validate every finding for exploitability, and prioritize fixes by business impact. You get a plan you can act on, not a 400-page scanner dump.
What does Assura deliver at the end of a penetration test?
Every engagement delivers step-by-step reproduction instructions for each finding, a plain-English attack narrative showing how separate issues chain into a real breach, and tailored remediation guidance prioritized by business impact. Findings are available in a secure reporting portal for a full year, with retesting available for any closed finding.
Can Assura test whether my security team actually detects an intrusion?
Yes. Assura can run engagements that deliberately probe whether your monitoring, SOC, or outside provider detects and responds to a real intrusion. If testers get in and out undetected, that is a finding in itself and a signal to evaluate your detection and response capabilities.
Does Assura's penetration testing satisfy regulatory and compliance requirements?
Yes. Assura scopes penetration tests to meet specific regulatory and contractual requirements including PCI DSS, HIPAA/HITECH, CMMC, SOC 2, NIST SP 800-53, and others. If your assessor or auditor finds the test does not satisfy that requirement, Assura fixes it at its own expense under the AuditArmor® Guarantee.
What is Penetration Testing-as-a-Service and when should I use it?
Penetration Testing-as-a-Service is a recurring testing program rather than a one-time engagement. It is best suited for organizations with active development pipelines, regulatory requirements for continuous testing, or mature security programs that need ongoing validation rather than a periodic point-in-time assessment.