
Powerful EDR is only half of it. The other half is the team that runs it.
Artificially intelligent endpoint security, managed by real humans in our SOC.
Your endpoints are where most breaches start, and where seconds matter. Modern EDR platforms block, kill, and contain threats autonomously in real time. Assura’s SOC is the team behind that automation: designing the policies that drive it, watching it every hour of every day, investigating what it cannot judge on its own, and owning the response. Powerful technology, managed by people who answer to you.
Attackers keep evolving. So should your defense.
Modern intrusions do not announce themselves. They abuse legitimate tools, move quietly from one machine to the next, and escalate while your team sleeps. A strong EDR platform will block and contain a great deal on its own, but it still surfaces alerts, ambiguous cases, and false positives that demand human judgment, and someone has to set the policies that govern it and watch it around the clock. The gap is rarely the tool. It is the trained team, available 24/7, to run it.
Detection, investigation, and response, fully managed.
Assura’s Managed Detection and Response service delivers continuous threat monitoring, investigation, and response across leading Endpoint Detection and Response (EDR) platforms. Our Security Operations Center handles the work end to end: expert triage, rapid alerting, swift remediation, and clear guidance on what happened and how to stay ahead of it.
AI-Powered Prevention at the Endpoint
Real-time autonomous blocking, malware remediation, network quarantine, and rollback before a threat can spread. The EDR acts instantly. Our SOC designed the policies that make it work.
Expert Triage, Not Alert Noise
Every alert is reviewed by Assura analysts who understand your environment. Our SOC separates real threats from false positives so your team is not chasing ghosts around the clock.
Response That Goes the Distance
From isolation to forensic analysis to remediation guidance, our SOC follows every confirmed incident through to resolution and tells you exactly what happened and how to prevent the next one.
Guaranteed compliance with these frameworks:
How we stop a threat.
Much of this happens autonomously and instantly at the endpoint. When a situation needs human judgment, every confirmed incident moves through the same disciplined path, run by Assura analysts.
- Initial Identification. A platform alarm, your report, or our own threat hunting surfaces suspicious activity.
- Investigate. Our SOC confirms whether it is a real threat and, where needed, works with your team to validate.
- Action. If it is valid, we remediate and report. If it is a false positive, we close it out, so your team is not chasing ghosts.
You choose how far our authority extends, from report-only, to automated quarantine, to full hands-on remediation. We work to your tolerance, not a one-size template.
Built for teams at every stage.
You inherited security. We'll help you own it.
For IT leaders and system administrators who are accountable for endpoint security without the headcount or specialized training the job requires. Assura’s MDR puts a 24/7 SOC behind every device so you get enterprise-grade detection and response without adding headcount. You focus on keeping the lights on. We focus on keeping threats out.
A partner who executes at your standard.
For CISOs and security program builders who need endpoint coverage they can defend to their board and that integrates with a broader program. Every response action is documented and every engagement is backed by committed SLAs.
Assura’s MDR operates under committed SLAs, documents every response action, and pairs cleanly with Managed SIEM/XDR for full-stack coverage.
Why Assura's MDR.
A SOC That Never Clocks Out
Assura’s SOC monitors your endpoints 24/7/365. Threats do not respect business hours, and neither do we. Every alert is investigated and triaged by experienced analysts, not queued for morning.
Platform Agnostic, Outcome Guaranteed
We work with the EDR you have or provide SentinelOne if you need it. The platform is flexible. The SLAs and the people behind them are not. And if your organization runs our Managed SIEM/XDR service, all endpoint telemetry flows directly into the Stellar Cyber platform, giving Assura’s SOC deeper visibility and faster response across your full attack surface.
Response, Not Just Reporting
Most MDR providers tell you something happened. Assura’s SOC contains it, remediates it, and tells you how to prevent the next one. You get the full picture, not just the alert.
Every MDR engagement is backed by the AuditArmor® Guarantee. If your audit reveals non-compliant work Assura performed, we fix it at our expense, no matter the cost.
Powered by SentinelOne and Huntress
Assura’s MDR service is built on SentinelOne’s AI-native endpoint protection platform and Huntress’s purpose-built managed EDR. SentinelOne’s autonomous response engine blocks, quarantines, and rolls back threats in real time. Huntress adds deep visibility into persistent footholds and post-exploitation activity that traditional EDR tools miss. Together they give Assura’s SOC the telemetry and response capability to stop threats across Windows, macOS, and Linux endpoints.
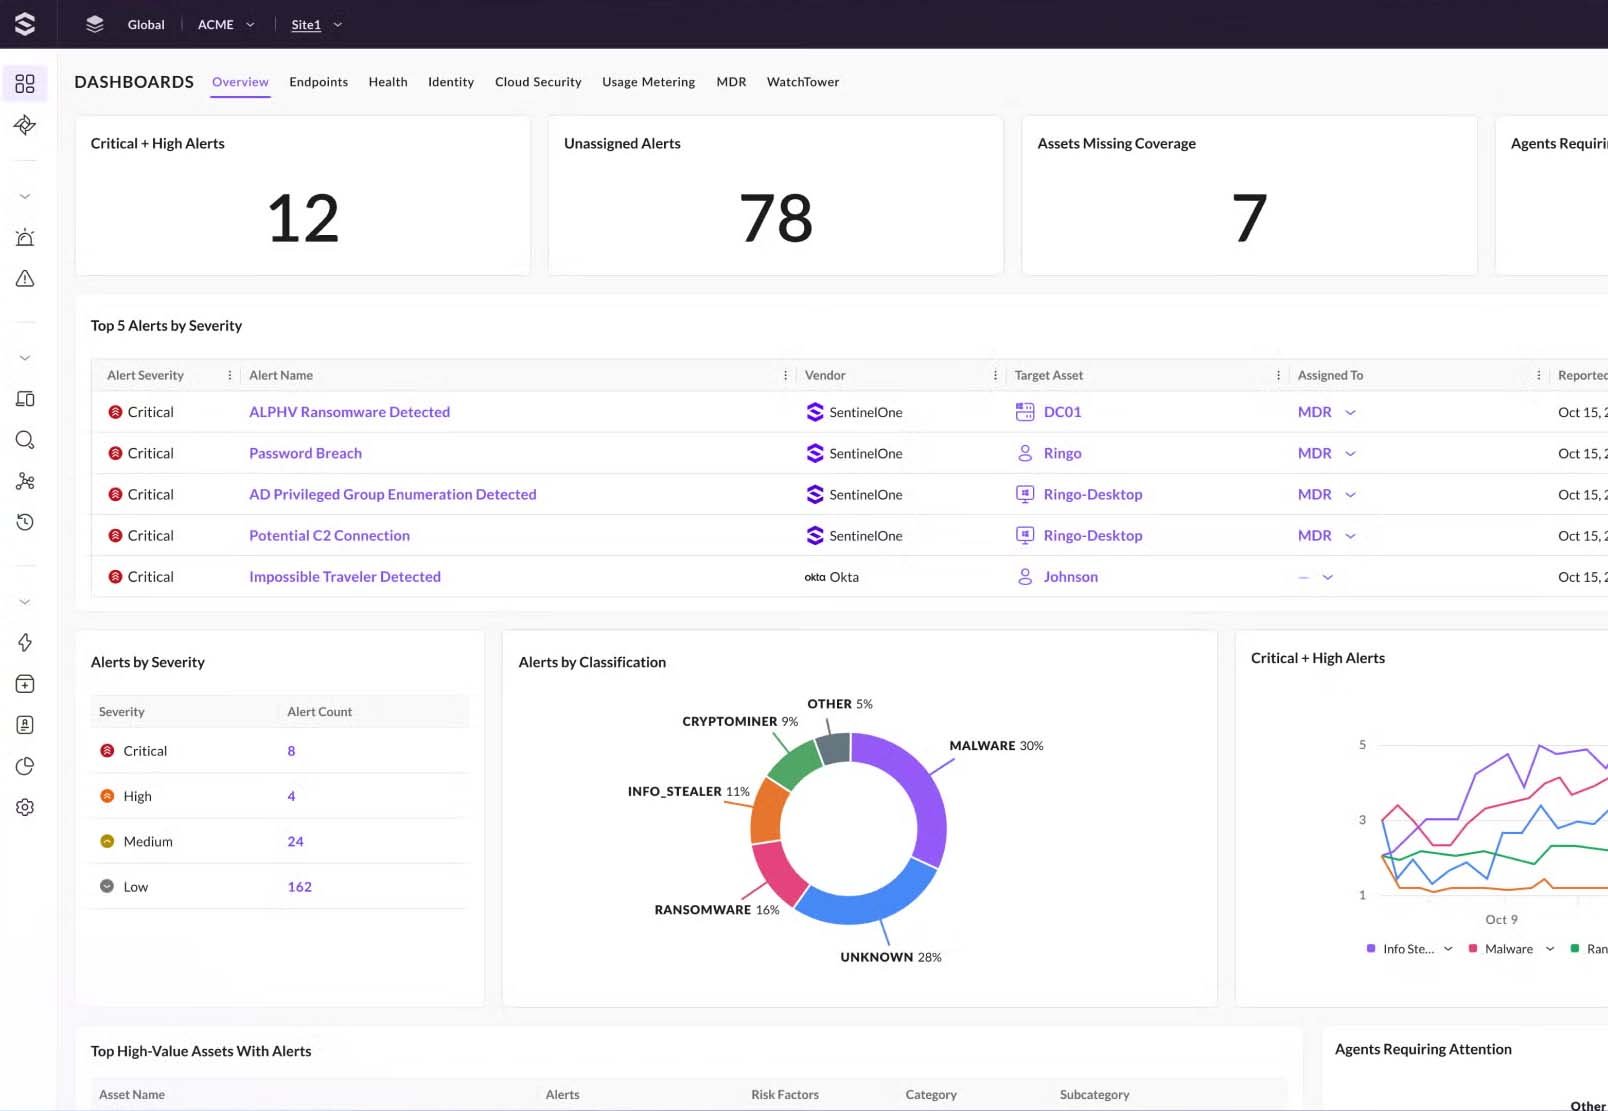
Signal, not noise.
Our worldwide sensor network analyzes hundreds of millions of events globally to surface the signals that matter to our clients.
24/7/365
Around-the-clock monitoring option
1 Hour
Committed initial response during service hours
19
Years defending our clients
Plans that fit how you want to run endpoint security.
Whichever plan you choose, Assura’s SOC is the constant. We design the policies, run the monitoring, and own the response and the relationship. The only thing that changes is whose endpoint technology sits underneath.
MDR with SentinelOne
Assura-Provided
The turnkey option. Nothing to procure. SentinelOne Control is licensed and provided by Assura, deployed, tuned, and managed by our SOC.
Best for: Organizations that want a single solution and a single invoice, with no EDR to source or manage.
What you get: Real-time autonomous prevention, malware remediation, network quarantine, and rollback at the endpoint, with the driving policies designed, tuned, and managed by our SOC.
MDR Bring Your Own License
BYOL
Keep the EDR you already invested in. Approved platforms: CrowdStrike Falcon Prevent, Huntress, Microsoft Defender for Endpoint, SentinelOne Control, SentinelOne Complete, and Sophos Intercept X.
Best for: Organizations with an existing EDR investment or licensing they want to keep using.
What you get: The same managed detection, investigation, and response, delivered on the platform you already own, with our SOC tuning the response policies and owning the outcome.
MDR with Huntress Overlay
Your Existing Endpoint Tool
Add managed detection without ripping out what you run. Huntress Managed EDR layered alongside your current endpoint tool, even one outside the approved BYOL list, across Windows, macOS, and Linux.
Best for: Organizations that cannot or will not replace their current endpoint software yet, but need real managed detection and response on top of it.
What you get: Huntress deployed alongside your existing tool, with Assura’s SOC operating the platform, running investigation and incident response, and owning the relationship. Huntress provides the added technology. Our analysts operate it, and you deal with Assura, not a vendor’s queue.
Let's lock down your endpoints.
Tell us how many endpoints you have and what you are running today. We will recommend the right plan and a path to coverage, usually within the same conversation.
Frequently Asked Questions
What is the difference between MDR and an EDR platform?
An EDR platform is technology. It detects threats, blocks malware, quarantines compromised assets, and in the case of SentinelOne, rolls back endpoints to their pre-attack state, all autonomously and in real time. But it still surfaces alerts, ambiguous cases, and false positives that require human judgment, and someone has to design the policies that govern it and watch it around the clock.
MDR is the managed service wrapped around that technology. Assura's SOC designs the policies, monitors every alert, investigates what the platform cannot judge on its own, and owns the response. The EDR is the engine. MDR is the team that runs it.
What is the difference between MDR and Managed SIEM/XDR?
MDR is focused on your endpoints: the laptops, desktops, and servers where an intrusion plays out. However an attacker gets in, whether through stolen credentials, a phishing click, or an exploited vulnerability, the endpoint is where they execute malware, escalate, and move laterally. Assura's SOC monitors, investigates, and responds to that activity using SentinelOne and Huntress.
Managed SIEM/XDR is broader. It ingests telemetry from your entire attack surface, including endpoints, networks, cloud, identity, and applications, and correlates it in a single platform. Where MDR gives you deep endpoint coverage, Managed SIEM/XDR gives you full-spectrum visibility across every layer of your environment.
The two services are designed to work together. When both are running, endpoint telemetry from MDR flows directly into the Stellar Cyber platform, giving Assura's SOC correlated visibility across your full attack surface rather than investigating endpoint and network threats as separate events.
Which EDR platforms does Assura support?
It depends on the plan. With MDR with SentinelOne, Assura provides the SentinelOne Control license, so there is nothing to procure. With MDR Bring Your Own License, you keep the EDR you already have. Approved BYOL platforms are CrowdStrike Falcon Prevent, Huntress, Microsoft Defender for Endpoint, SentinelOne Control, SentinelOne Complete, and Sophos Intercept X. With MDR with Huntress Overlay, Huntress Managed EDR is deployed alongside your existing endpoint tool, even one outside the approved BYOL list, across Windows, macOS, and Linux. If you are not sure which plan fits your current stack, that is exactly what the scoping conversation is for.
What is the difference between the three MDR plans?
All three plans put Assura's SOC in the same role: constructing the policies, running the monitoring, and owning the response. What changes is whose endpoint technology sits underneath.
MDR with SentinelOne is the turnkey option. Assura provides the SentinelOne Control license, deploys it, and manages it end to end. Nothing to procure, nothing to source.
MDR Bring Your Own License is for organizations with an existing EDR investment they want to keep. Assura's SOC operates your platform, tunes the response policies, and owns the outcome on the approved EDR you already have.
MDR with Huntress Overlay is for organizations that cannot or will not replace their current endpoint software yet but need real managed detection and response on top of it. Huntress is deployed alongside your existing tool, across Windows, macOS, and Linux, with Assura's SOC operating the platform and owning the relationship.
How much control do we have over how Assura responds to a threat?
You choose how far our authority extends. At one end, we operate in report-only mode: we investigate, tell you what we found, and you decide what to do. At the other end, we have full hands-on remediation authority: we contain, remediate, and tell you what we did. Most clients land somewhere in between, authorizing automated quarantine for confirmed threats while retaining approval for more disruptive actions. We work to your tolerance, and the authority model is defined and documented at the start of the service.