
Your network deserves a watchdog that never sleeps.
When a threat enters your environment, the clock starts. Our Managed SIEM/XDR service identifies, investigates, and responds to threats across your entire attack surface 24/7/365, backed by the most advanced AI-native NextGen SIEM and XDR platform on the market.
Threats don't wait for business hours. Your monitoring shouldn't either.
Most IT and security teams are stretched across operations, compliance, and incident response simultaneously. Disconnected tools generate alert noise without context, and without continuous expert-led monitoring, the gap between “something happened” and “we knew about it” is exactly where breaches live. Your organization is generating security events right now. The question is whether anyone is watching, investigating, and responding.
What Assura's Managed SIEM/XDR delivers.
Continuous monitoring, expert investigation, and automated response, delivered as a fully managed service so your team can focus on what matters most.
Full-Spectrum Visibility
Managed log and telemetry collection and monitoring across your entire attack surface, including endpoints, networks, cloud, identity, and applications, unified in a single platform.
Signal, Not Noise
Our NextGen SIEM/XDR platform’s ML-powered detection, combined with active, real-time threat hunting and Assura’s expert SOC, produces actionable, high-fidelity alerts, not alert fatigue. Every detection is triaged by humans who understand your environment.
Automated Response
AI-driven threat blocking and automated playbooks stop threat actors before they can move laterally. When our SOC detects a threat, we don’t just notify you, we act.
Guaranteed compliance with these frameworks:
Built for teams at every stage.
You inherited security. We'll help you own it.
For IT leaders and system administrators who are accountable for security outcomes without the headcount or specialized training the job requires. Assura’s SOC becomes your security team by monitoring, triaging, and responding around the clock so you can focus on keeping the lights on. No additional headcount required.
A partner who executes at your standard.
For CISOs and security program builders who need a high-fidelity, low-noise extension of their program. MITRE ATT&CK-aligned coverage, a SOC that integrates without creating management overhead, and outcomes you can defend to your board.
Building toward SOC 2 Type II? Managed SIEM/XDR satisfies the continuous monitoring controls your auditor requires. Pair it with GRC-as-a-Service for a complete compliance program.
Why Assura's Managed SIEM/XDR.
A SOC That Never Clocks Out
Assura’s SOC operates 24/7/365. Threats don’t respect business hours, and neither do we. Every alert is investigated and triaged by experienced analysts, not just logged and queued for morning.
Machine Intelligence, Human Judgment
Multi-Layer AI™ detects threats across the kill chain. Assura’s analysts investigate, validate, and respond. The result is high-fidelity detection with human accountability behind every action taken.
Open XDR: No Vendor Lock-In
Our NextGen SIEM/XDR platform’s architecture ingests telemetry from your existing security tools, including endpoints, firewalls, identity, cloud, without requiring you to rip and replace. Your stack, unified.
If your organization runs our Managed MFA service, Duo authentication logs flow directly into the platform, giving our analysts identity context on every alert. If you run our Vulnerability Management-as-a-Service, scan findings from Tenable or Rapid7 feed in as well, so our SOC can correlate active vulnerabilities with live threat activity. And if you use our email security service, phishing detections feed in too, so a suspicious email and a suspicious login do not get investigated as two separate events.
Every Managed SIEM/XDR engagement is backed by the AuditArmor® Guarantee. If your audit reveals non-compliant work Assura performed, we fix it at our expense, no matter the cost.
Powered by Stellar Cyber Open XDR
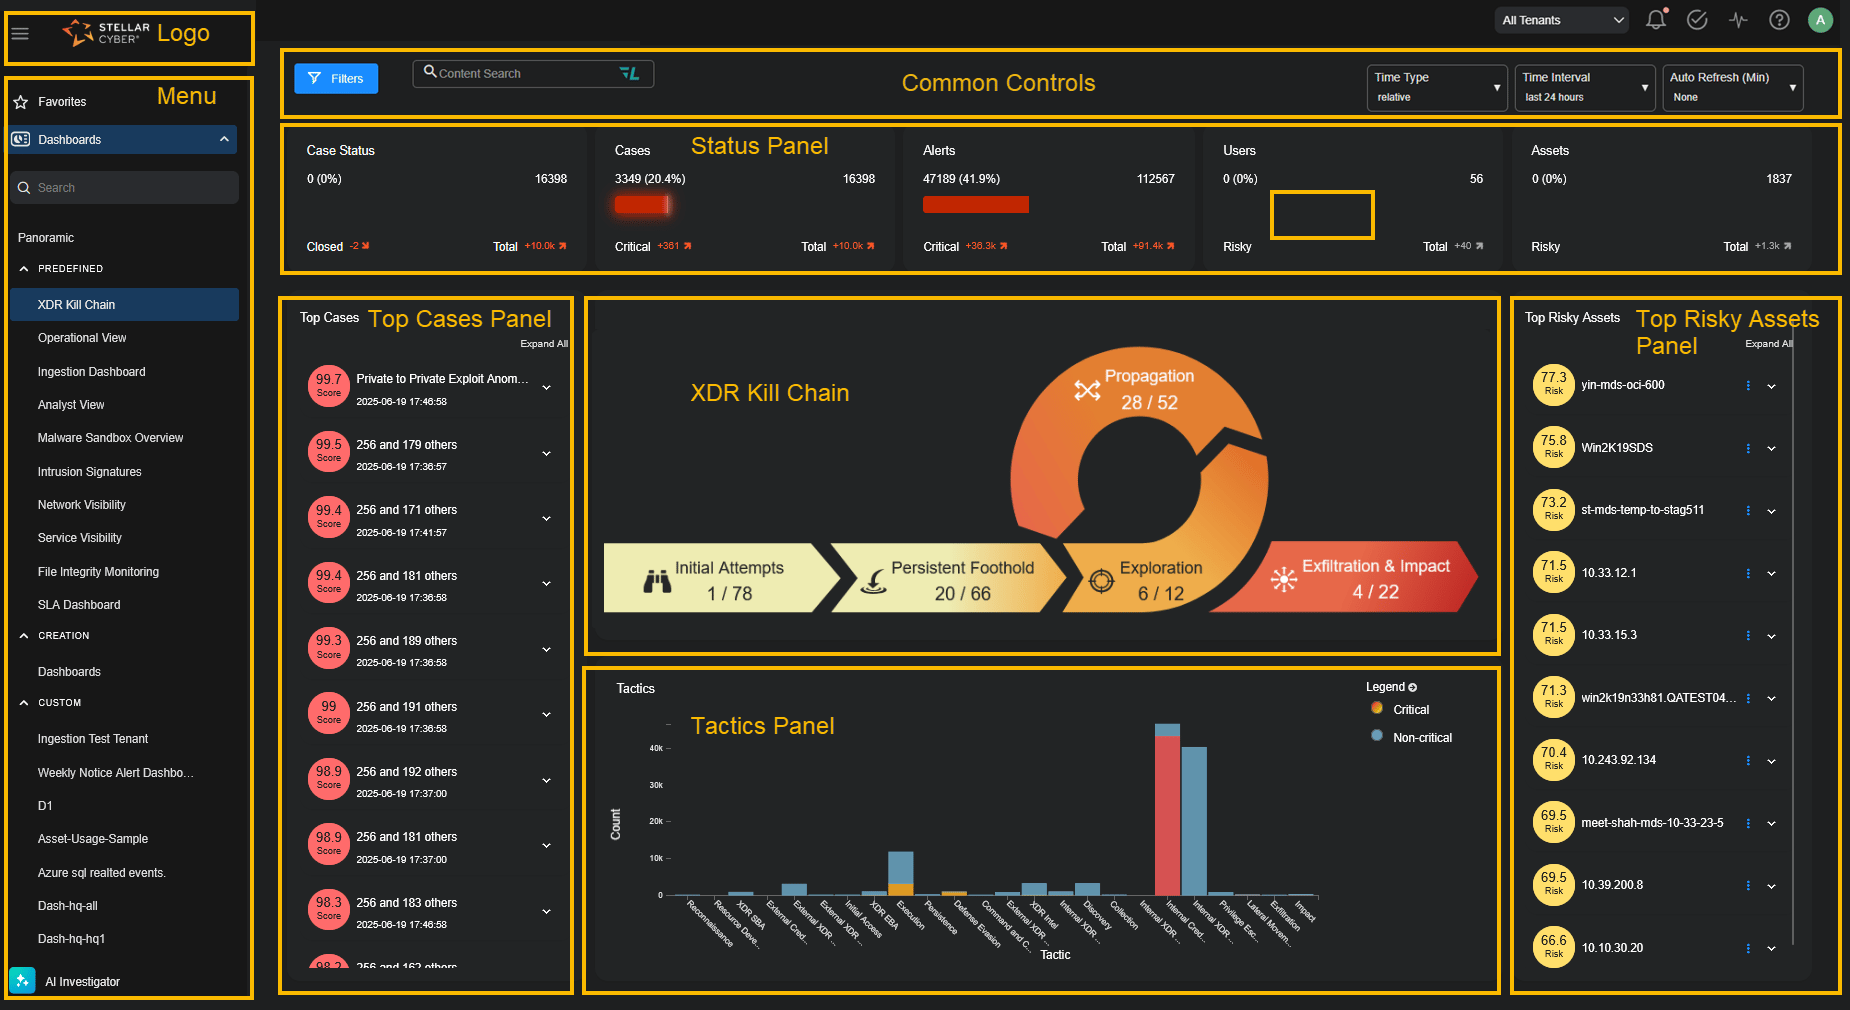
Stellar Cyber’s Open XDR platform provides a single unified view across your entire attack surface. Multi-Layer AI™ correlates signals from endpoints, networks, cloud, identity, and applications, mapping threats to the XDR Kill Chain in real time so Assura’s SOC always knows where an attacker is and what they’re doing next.
This includes authentication events from Cisco Duo, vulnerability findings from Tenable and Rapid7, phishing detections from your email security platform, and telemetry from your EDR, firewall, cloud, and identity platforms, all correlated in a single view so nothing is investigated in isolation.
Real threats. Real resolution.
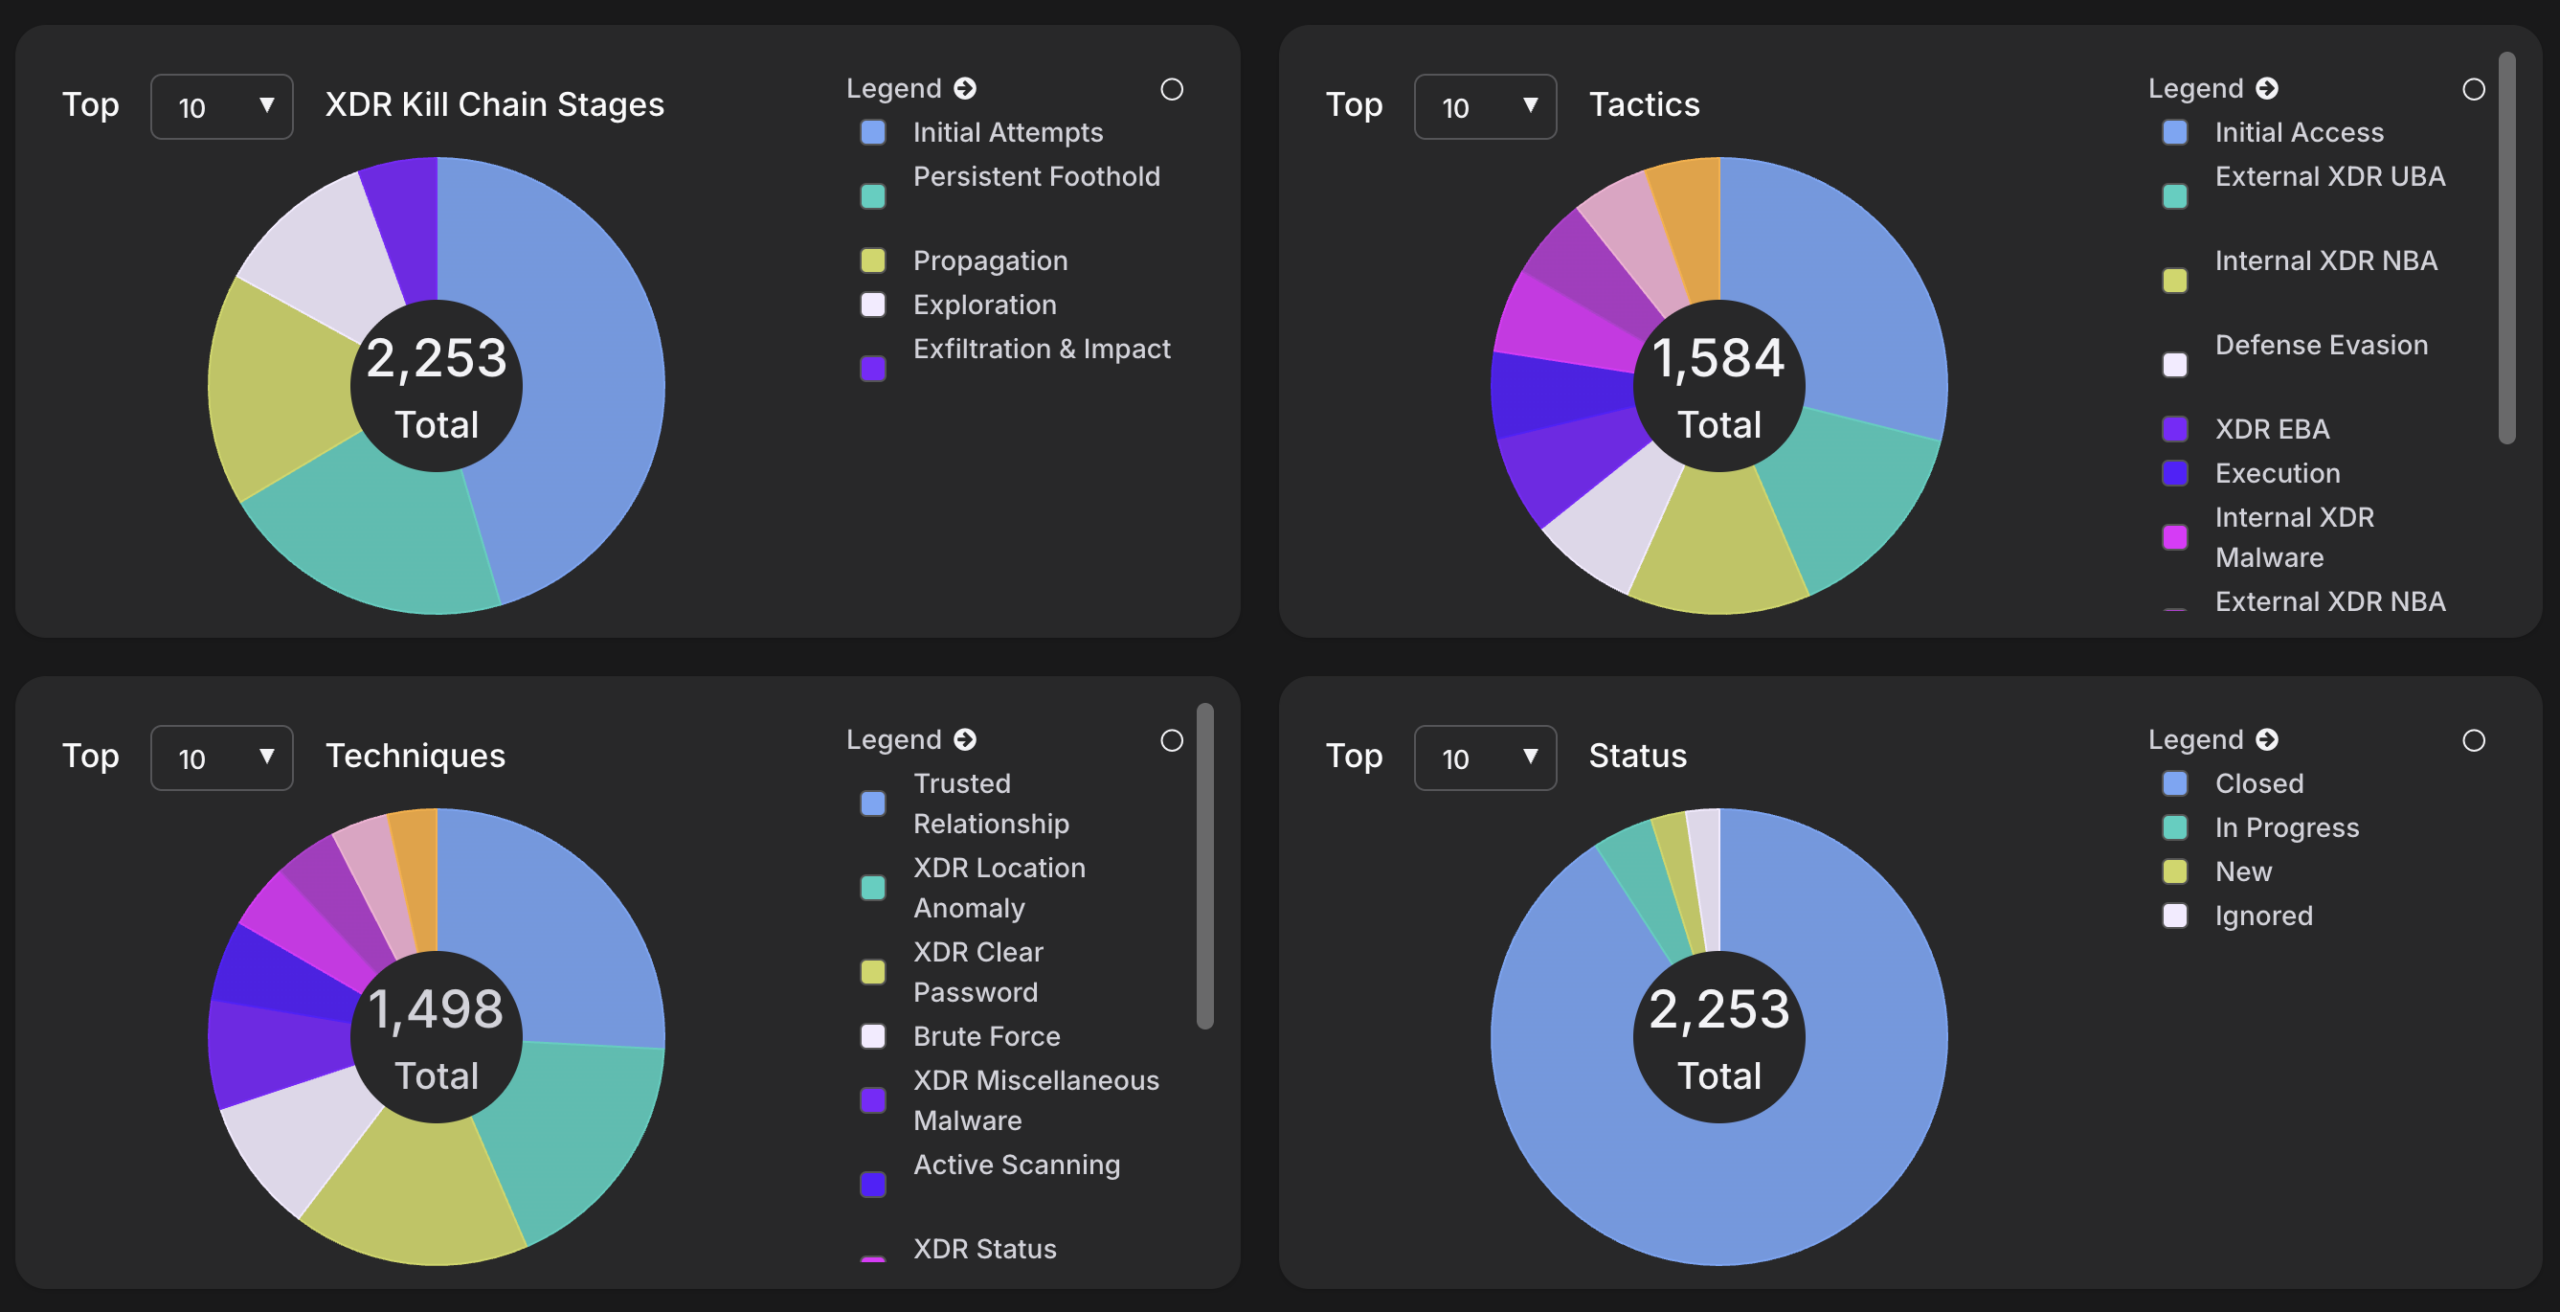
Every alert in Assura’s SOC is triaged, investigated, and actioned, not just logged. The dashboard below reflects live data from our SOC: thousands of alerts classified by MITRE ATT&CK kill chain stage, tactic, and technique, with the majority resolved.
24/7/365
SOC monitoring and response,
every day of the year
20+
Compliance frameworks covered under the AuditArmor® Guarantee
19 Years
Protecting clients across sectors and industries
Plans that meet any organization's need.
Kickstarter
Excellent for small enterprises.
- Business hours investigation and reporting SLA
- Managed log collection and monitoring
- Active hunting for threats in your environment
- Root cause analysis
- Dedicated portal with reporting dashboard and analytics
Sentry
Enhanced SLA and cybersecurity insights.
Everything in Kickstarter, plus:
- 24/7/365 investigation and reporting SLA
- Monthly service reporting with expert trend analysis and recommendations to improve your security posture
Shield
Neutralizes threats.
Everything in Sentry, plus:
- AI-driven threat blocking
- Incident response
- Remote forensic analysis
- Automated playbooks stop threat actors in their tracks
Ready to put a watchdog on your network?
Talk to Assura’s team about the right plan for you.
Frequently Asked Questions
What is the difference between a SIEM and XDR?
A SIEM (Security Information and Event Management) collects, normalizes, and analyzes log and event data from across your environment to detect threats, support investigation, and produce the reporting that compliance frameworks require. It has been the foundation of security monitoring for decades and is often deployed primarily to satisfy compliance requirements, but traditional SIEMs generate high volumes of alerts that demand significant analyst time to triage.
XDR (Extended Detection and Response) grew out of endpoint detection and response. It correlates telemetry across multiple layers, endpoints, networks, cloud, identity, and applications, and applies analytics to turn signals from those separate sources into fewer, higher-fidelity detections. Where a traditional SIEM is oriented toward collecting data and reporting on it, XDR is oriented toward detecting and responding to active threats.
Modern platforms increasingly combine both: the log collection and compliance reporting of a SIEM with the cross-layer correlation and threat focus of XDR. The platform behind Assura's service is one of them, which is why this service is described as Managed SIEM/XDR rather than one or the other.
What is Open XDR and why does it matter?
Open XDR is an approach to XDR that ingests telemetry from the security tools you already run, regardless of vendor, rather than requiring you to replace them with a single vendor's stack. A closed, or native, XDR works only with its own vendor's components. Open XDR is built to correlate signals across a mixed environment.
It matters because most organizations have already invested in endpoint, firewall, identity, and cloud tools from different vendors. An Open XDR approach unifies the telemetry from all of them into one correlated view without a rip-and-replace. Your existing stack keeps working, and you gain cross-layer detection on top of it.
For Assura's service, this is what lets our SOC bring your current tools into a single view rather than asking you to start over. We operate the platform, tune the detections for your environment, and investigate what matters. How far we take the response depends on your tier: at every level we detect, investigate, and report, and at the Shield tier we also contain threats and provide remote forensic analysis. What you buy is a managed outcome, not a tool to run yourself.
What is the difference between the three tiers?
All three tiers include managed log collection and monitoring, active threat hunting, root cause analysis, and a dedicated reporting portal. What changes is the SLA and what Assura does when a threat is confirmed.
Kickstarter is built for smaller organizations and operates on a business hours investigation and reporting SLA. It is the right starting point when you need continuous monitoring and expert threat hunting without the cost of round-the-clock coverage.
Sentry adds 24/7 SLA coverage and monthly service reporting with expert trend analysis and recommendations. The right choice when continuous monitoring needs to be backed by a round-the-clock response commitment.
Shield adds AI-driven threat blocking, incident response, remote forensic analysis, and automated playbooks. At Shield, Assura does not just detect and report, we contain and remediate. The right choice when your environment demands the full managed response capability, not just visibility and alerting.
How does Managed SIEM/XDR integrate with our other security tools?
The platform ingests telemetry from your existing security tools without requiring you to replace them. Firewalls, endpoints, cloud environments, identity providers, and applications all feed into a single correlated view. If you run Assura's other services, the integrations go deeper: Duo authentication logs from our Managed MFA service feed in automatically, giving our SOC identity context on every alert. Vulnerability scan findings from a VMaaS engagement feed in as well, so our SOC can correlate active vulnerabilities with live threat activity. And phishing detections from our Managed Email Security service feed in too, so a suspicious email and a suspicious login are investigated together rather than as two separate events.
If you use security tools outside the Assura stack, our SOC works with your team to onboard them into the platform. The goal is one correlated view across everything, not a parallel system that ignores what you already have.
What is MITRE ATT&CK and why does it matter for monitoring?
MITRE ATT&CK is a publicly maintained knowledge base of adversary tactics, techniques, and procedures (TTPs), built from real-world observations of how attackers actually behave. It organizes attacker behavior into a framework of tactics, each representing a stage of an intrusion, such as initial access, lateral movement, and exfiltration, and techniques, which are the specific methods attackers use within each stage.
It matters for monitoring because it gives Assura's SOC a shared, structured language for describing where an attacker is in an intrusion and what they are likely to do next. When our platform maps a detection to a MITRE ATT&CK tactic and technique, it tells our analysts not just that something happened, but where it fits in the attack chain, which shapes the investigation and the response. It also means the detections covering your environment can be measured against a known, comprehensive framework rather than a proprietary list, so you can have confidence in what is and is not being watched for.