
Compliance isn't a project. It's a program. Treat it like one.
A defensible cybersecurity program, continuously managed and backed by a written guarantee.
Most GRC programs don't fail because of hackers. They fail before the hackers arrive.
Your cybersecurity program probably started the same way most do. A breach, an audit finding, or a new regulatory requirement arrived, and security got handed to IT. Policies were written. Tools were purchased. And every year, the same findings come back.
The problem isn’t effort. It’s ownership. Without a dedicated program leader, continuous monitoring, and executive-level visibility, compliance becomes a fire drill and protection becomes an afterthought.
A continuously managed GRC program, run by your team at Assura.
GRC-as-a-Service combines senior cybersecurity expertise, an analyst team dedicated to your success, and an agentic AI-driven automation platform to deliver a program that runs every day, not just at audit time.
Senior Virtual ISO
A CISO-level program leader assigned to your account. Sets strategy, owns audit defense, reports to your executives, and makes the risk trade-offs your organization needs to see in business terms.
Virtual ISOs
Your team of dedicated cybersecurity analysts. Manages policies, evidence collection, and remediation tasks. Keeps the program moving between audits so nothing drifts.
Continuous Monitoring Platform
Real-time control measurement, automated evidence collection, and executive dashboards powered by our agentic AI-driven automation platform. Surface control drift in days, not at next year’s audit.
Guaranteed compliance with these frameworks:
Built for leaders who are accountable for security outcomes.
For the Compliance-Accountable Executive
You are responsible for audit results, regulatory compliance, and board-level reporting. You have seen what happens when a finding recurs for the third year in a row. GRC-as-a-Service gives you one accountable owner for the program, measurable progress you can report upward, and a written guarantee on the work we perform.
For the IT Leader Who Inherited Security
If you inherited security along with your IT responsibilities, GRC-as-a-Service gives you a team that handles the program without requiring you to become a compliance expert. You stay engaged. We do the heavy lifting.
Why organizations choose Assura for GRC.
We meet you where you are.
We build on what’s working and replace what isn’t, rather than imposing a one-size-fits-all program. Your first 90 days move from kickoff to a measurable, defensible posture.
Management, technical, and operational controls, together.
Most programs cover one or two. We integrate all three, so controls actually hold between audits, not just during them.
Nineteen years of GRC delivery, backed by a written guarantee.
We have been doing this since 2007. On Managed and Advanced tiers, every control we manage is covered by our AuditArmor® Guarantee.
If your audit reveals non-compliant work Assura performed, we fix it at our expense, no matter the cost. That’s the AuditArmor® Guarantee.
See your compliance posture in real time.
On all tiers, every control in your environment is tracked, measured, and evidenced through our agentic AI-driven automation platform. When your auditor arrives, the evidence is organized, the testing is documented, and the path to a conclusion is already clear. Faster audits, fewer disruptions, less exposure.
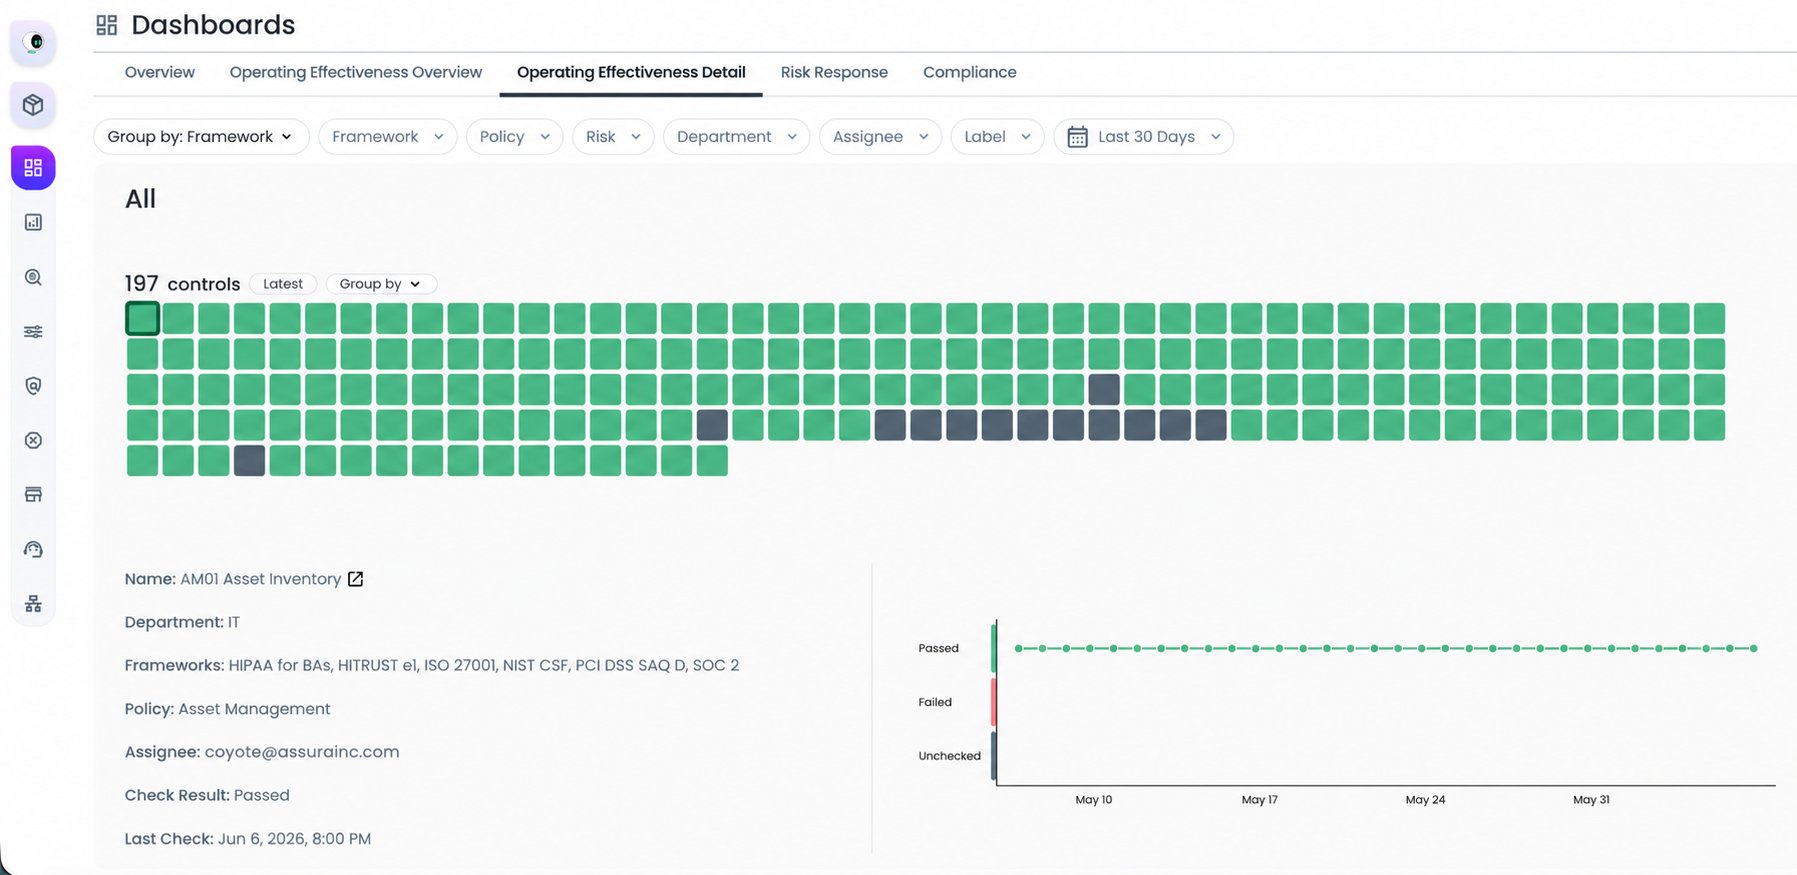
What a managed GRC program looks like in practice.
“For the first time, our board sees cybersecurity as a managed program with measurable progress, not a list of overdue findings.”
Director of IT, public-sector Assura client
Zero audit findings carried forward across consecutive cycles for managed-program clients.
Days to surface a control drift, instead of waiting for the next annual audit.
One accountable owner for your cybersecurity program: your Senior Virtual ISO.
Three ways to engage.
Essentials
You own and execute the program. We show you the path and guide you down it: the platform, the frameworks, the templates, and on-demand access to a Senior Virtual ISO when you need expert judgment. Best for organizations with internal GRC capacity who want expert backing.
Managed
You own the program. We lead you down the path with hands-on execution. A dedicated Virtual ISO manages your day-to-day program. A Senior Virtual ISO sets direction and defends the audit. Best for programs that need real execution, not just advice. Covered by the AuditArmor® Guarantee.
Advanced
You own the program. We lead it end to end. A Senior Virtual ISO is your functional program leader and primary executor, supported by a Virtual ISO for compliance maintenance. Best for complex environments or organizations needing a fast program build. Covered by the AuditArmor® Guarantee.
Annual commitment required. Flexible billing options. Multi-year price-lock available.
Let's spend 60 minutes on your program.
We will walk through your environment, understand your risks, and tell you honestly where you stand. No sales pitch, no obligation.
Frequently Asked Questions
What is the difference between GRC-as-a-Service and a one-time Security Program Development engagement?
Security Program Development is a project. We produce the specific deliverables you need: a gap analysis, policies, a risk assessment, an incident response plan, etc. Then we conduct knowledge transfer and hand them off for your team to own and operate.
Conversely, GRC-as-a-Service is ongoing. An expert Assura team runs the program day-to-day, maintains your evidence between audits, and defends the work when an auditor arrives.
Choose Security Program Development when you have the internal capacity to run what we build. Choose GRC-as-a-Service when you want the program owned and operated for you.
What is the difference between a Virtual ISO and a Senior Virtual ISO?
A Senior Virtual ISO from Assura is your CISO-level program leader. They set strategy, own audit defense, suggest risk trade-offs, and report to your executives. A Virtual ISO is a skilled compliance analyst assigned to carry out one or more program-building or operational responsibilities. They manage policies, collect evidence, and keep remediation moving between audits. At the Managed tier, you get both roles. At Advanced, the Senior Virtual ISO steps into a more hands-on leadership and execution role.
Is the AuditArmor® Guarantee included in every tier?
No. The AuditArmor® Guarantee only covers the work Assura performs. At the Managed and Advanced tiers, Assura builds, executes, and manages controls, so the guarantee applies.
At the Essentials tier, your team owns and executes the program, with Assura providing the platform, frameworks, templates, and on-demand access to Virtual ISOs and Senior Virtual ISOs. Because your team is performing the work, there is nothing for the guarantee to attach to.
If a written guarantee on the work matters to you, the Managed or Advanced tiers are right for you.
Will you replace the security tools and processes we already have?
No. We build on what is already working and replace only what is not. Your first ninety days move from kickoff to a measurable, defensible posture using your existing investments wherever they hold up, so you are not paying to rebuild controls you already have.
Do we still need internal security staff if we use GRC-as-a-Service?
It depends on the tier. At the Managed and Advanced tiers, you stay engaged but you do not need a compliance expert on payroll. Your Assura team does the heavy lifting: running the program, collecting evidence, and preparing for audits. Your role is to make the business decisions only you can make and to give us access to the people and systems the program touches.
At the Essentials tier, your team owns execution, so some internal capacity to carry out program tasks is expected.
Many of our clients are IT leaders who inherited security and have no room to add headcount, which is often what drives them toward Managed or Advanced.