
When the auditor arrives, so do we.
AuditArmor® Audit Defense puts Assura in the room for your scheduled audit or examination, from the entrance conference to the final remediation plan. We defend the work we did. We help you navigate the rest.
An audit rewards preparation as much as compliance.
Good auditors, and most are, want the process to go well. They are not looking for a fight, they are looking for evidence, context, and a straight answer. But even the most collaborative audit still runs on judgment. A finding can be recorded as a minor observation or a significant deficiency, and that often comes down to how clearly it is presented, contextualized, and responded to.
If Assura built the program you are being audited against, we already know it, and we already speak the auditor’s language. We show up at the entrance conference, we participate in the walkthroughs, and we make sure the conversation stays focused on what is actually in scope, not because anyone is trying to pull a fast one, but because a scoped engagement keeps everyone’s time well spent. When findings come up, we help you respond to them clearly and accurately, so the record reflects the reality of your program.
Assura’s audit defense clients are being examined against frameworks including:
Not sure if you are ready for the audit yet?
Our Compliance Gap Analysis acts as an audit readiness review and can tell you where you stand before the auditor does.
What Assura does during your audit.
Pre-Audit Preparation
Before the auditor arrives, we make sure everyone is working from the same understanding. We review scope, confirm documentation is ready, and align expectations with your team so there are no surprises on day one.
Entrance Conference and Walkthroughs
We are in the room from the first meeting. Assura participates in every technical and procedural walkthrough, answering directly for the work we performed and providing context for everything else.
Scope Management
Audits run best when they stay focused on what was actually agreed to. We help keep the engagement on track, so time is spent on what matters and the process stays efficient for everyone involved.
Brief Out and Management Responses
When preliminary findings are delivered, we are there to hear them first. In most cases, Assura drafts the management responses for your review and approval, because how a finding is presented affects how it is ultimately recorded.
Remediation
If a finding needs to be addressed, we help close it.
Scope, built into the engagement.
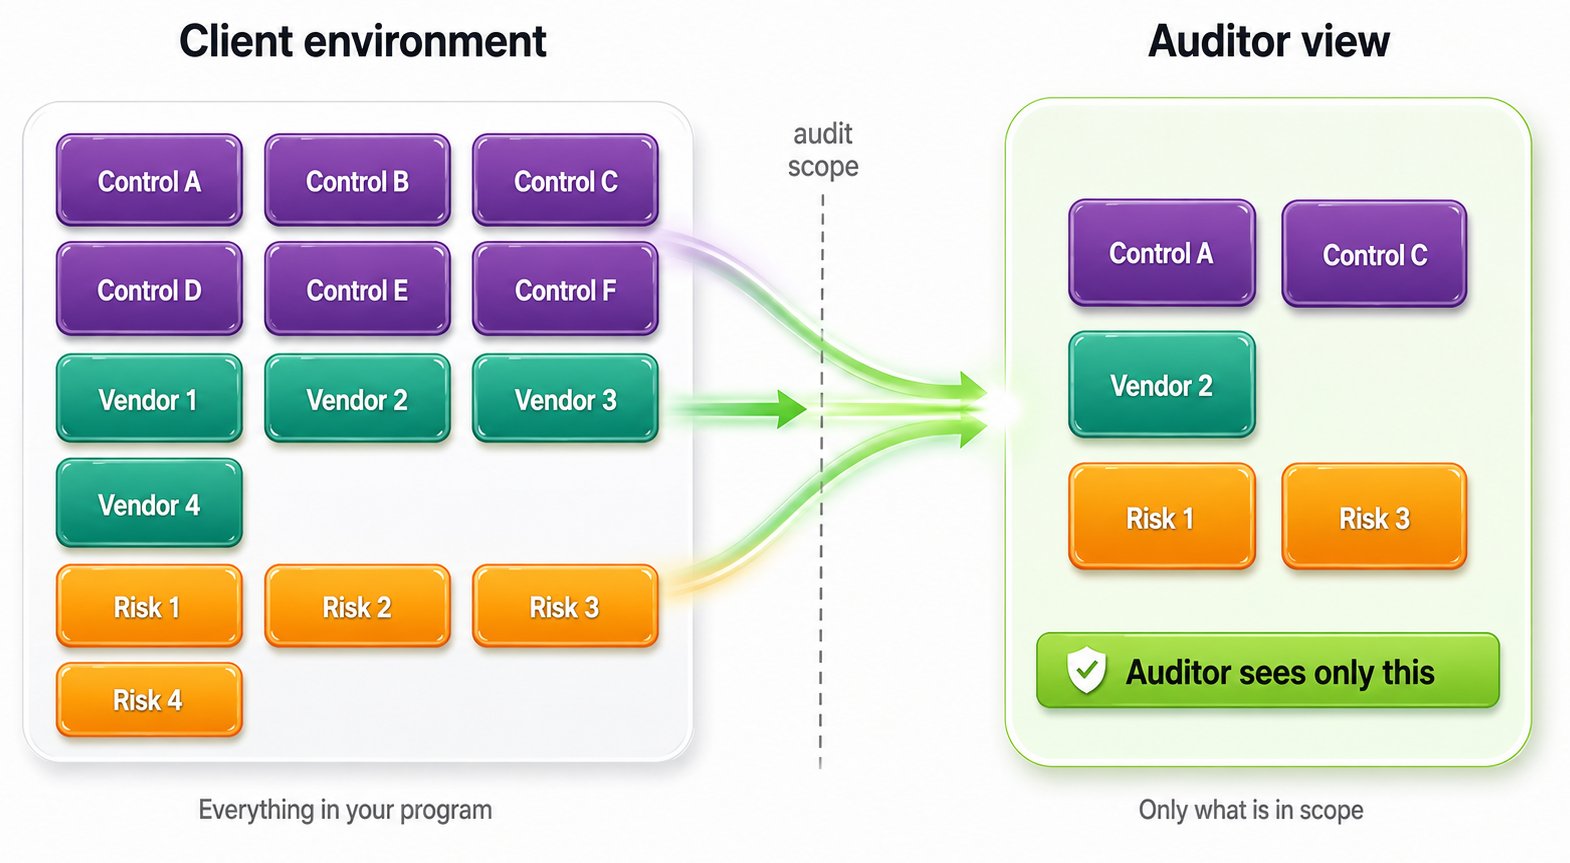
For clients on our GRC-as-a-Service, we build a dedicated audit project in our agentic AI-driven automation platform and link only the controls, third-party vendors, and risks that are in scope. The auditor works from that curated view, so the examination stays focused on what was agreed to and nothing outside it.
Who this is for.
The executive accountable for the outcome.
You are accountable for how this audit turns out, and a bad result does not stay contained to security. It becomes a board conversation. Having Assura in the room means you are not the only one carrying that weight.
The security leader who still has a day job.
You cannot sit through every walkthrough, manage auditor requests, and draft airtight management responses without something else slipping. We handle the documentation work and the response drafting so you stay informed without being buried.
The IT leader who owns the environment, not the audit process.
You know the systems, the controls, and how everything fits together. What an audit adds is a formal examination process with its own conventions, its own language, and its own dynamics. We handle that layer so you can focus on what you actually know best.
The founder whose deal depends on the cert.
If a SOC 2 or CMMC audit is what stands between you and closing, a mishandled finding can cost you the deal, not just the certification. We make sure the audit moves as fast and cleanly as the deal needs it to.
We already know the answer, because we already did the work.
Plenty of firms will sit in on your audit. Far fewer built the systems and programs being examined. When Assura performed the work under review, we are not learning your environment during the entrance conference, we already know it, because we built it. There is no ramp-up and no guessing what the auditor is going to ask.
That same standing carries into findings outside our own work. Auditors respond to a team that clearly knows what it is talking about, and that credibility is what lets us negotiate a finding, contextualize a gap, or push back on scope creep effectively, even when the issue in question has nothing to do with anything Assura built.
This is what our AuditArmor® Guarantee looks like in practice.
Assura fixes the compliance variance at our own expense, no matter the cost. That’s the AuditArmor® Guarantee. Audit Defense is how that promise gets kept. We do not wait for a finding to become a problem, we are in the room when it surfaces, and if the finding traces back to work we performed, we make it right.
Have an audit on the calendar?
If Assura already works with your organization, talk to your account team about bringing us into your next audit or examination. If you are not yet a client and this is the kind of protection you are looking for, let’s talk about what an ongoing relationship with Assura could look like.
Frequently Asked Questions
What is the difference between Audit Defense and the AuditArmor® Guarantee?
The AuditArmor® Guarantee is a contractual warranty: if your audit reveals non-compliant work Assura performed, we fix the variance at our expense, no matter the cost. Audit Defense is the service that puts us in the room when your audit happens, defending the work we performed from the entrance conference through remediation. The guarantee is the promise. Audit Defense is how we stand behind it in real time.
Can Assura defend our audit even if Assura did not build the program?
Yes. When Assura built the program under review, there is no ramp-up, because we already know your environment. But our value in the room carries into findings outside our own work too. Auditors respond to a team that clearly knows what it is talking about, and that credibility lets us contextualize a gap, negotiate how a finding is recorded, or push back on scope creep, even when the issue has nothing to do with anything Assura built.
What is the difference between an audit and an examination?
In practice they refer to the same thing: a formal, independent review of your controls against a standard. Different frameworks and regulators use different words. Financial regulators tend to say "examination," while SOC 2, ISO, and CMMC contexts tend to say "audit" or "assessment." Whatever your framework calls it, Audit Defense works the same way.
Can we engage Audit Defense if we are not already an Assura client?
Audit Defense is available to existing Assura clients only. Because we are defending work we performed and a program we know, we need to have an established relationship with your organization before your audit begins. If you are not yet a client and have an audit on the horizon, the right first step is a discovery conversation about what an ongoing relationship with Assura could look like. The earlier we are involved, the more we can do before the auditor arrives.
What if we are not sure we are ready for the audit yet?
Before you defend an audit, you can find out where you stand. A Compliance Gap Analysis acts as an audit readiness review, measuring your current state against the framework you will be examined against and showing you the gaps while there is still time to close them. It is often the right first step when an audit is on the horizon but not yet scheduled.